Build your SecOps, trading, bidding, monitoring or integration agent. Your CISO, chief compliance officer, CMO, COO or CTO can approve it.
The enterprise-ready platform for high-performance, mission-critical agents.
- Built-in agent modelReads your memory first
- Workflows that don’t driftKnown path, every time
- Enterprise memoryCases · procedures
- Governance on every actionCedar · deny by default
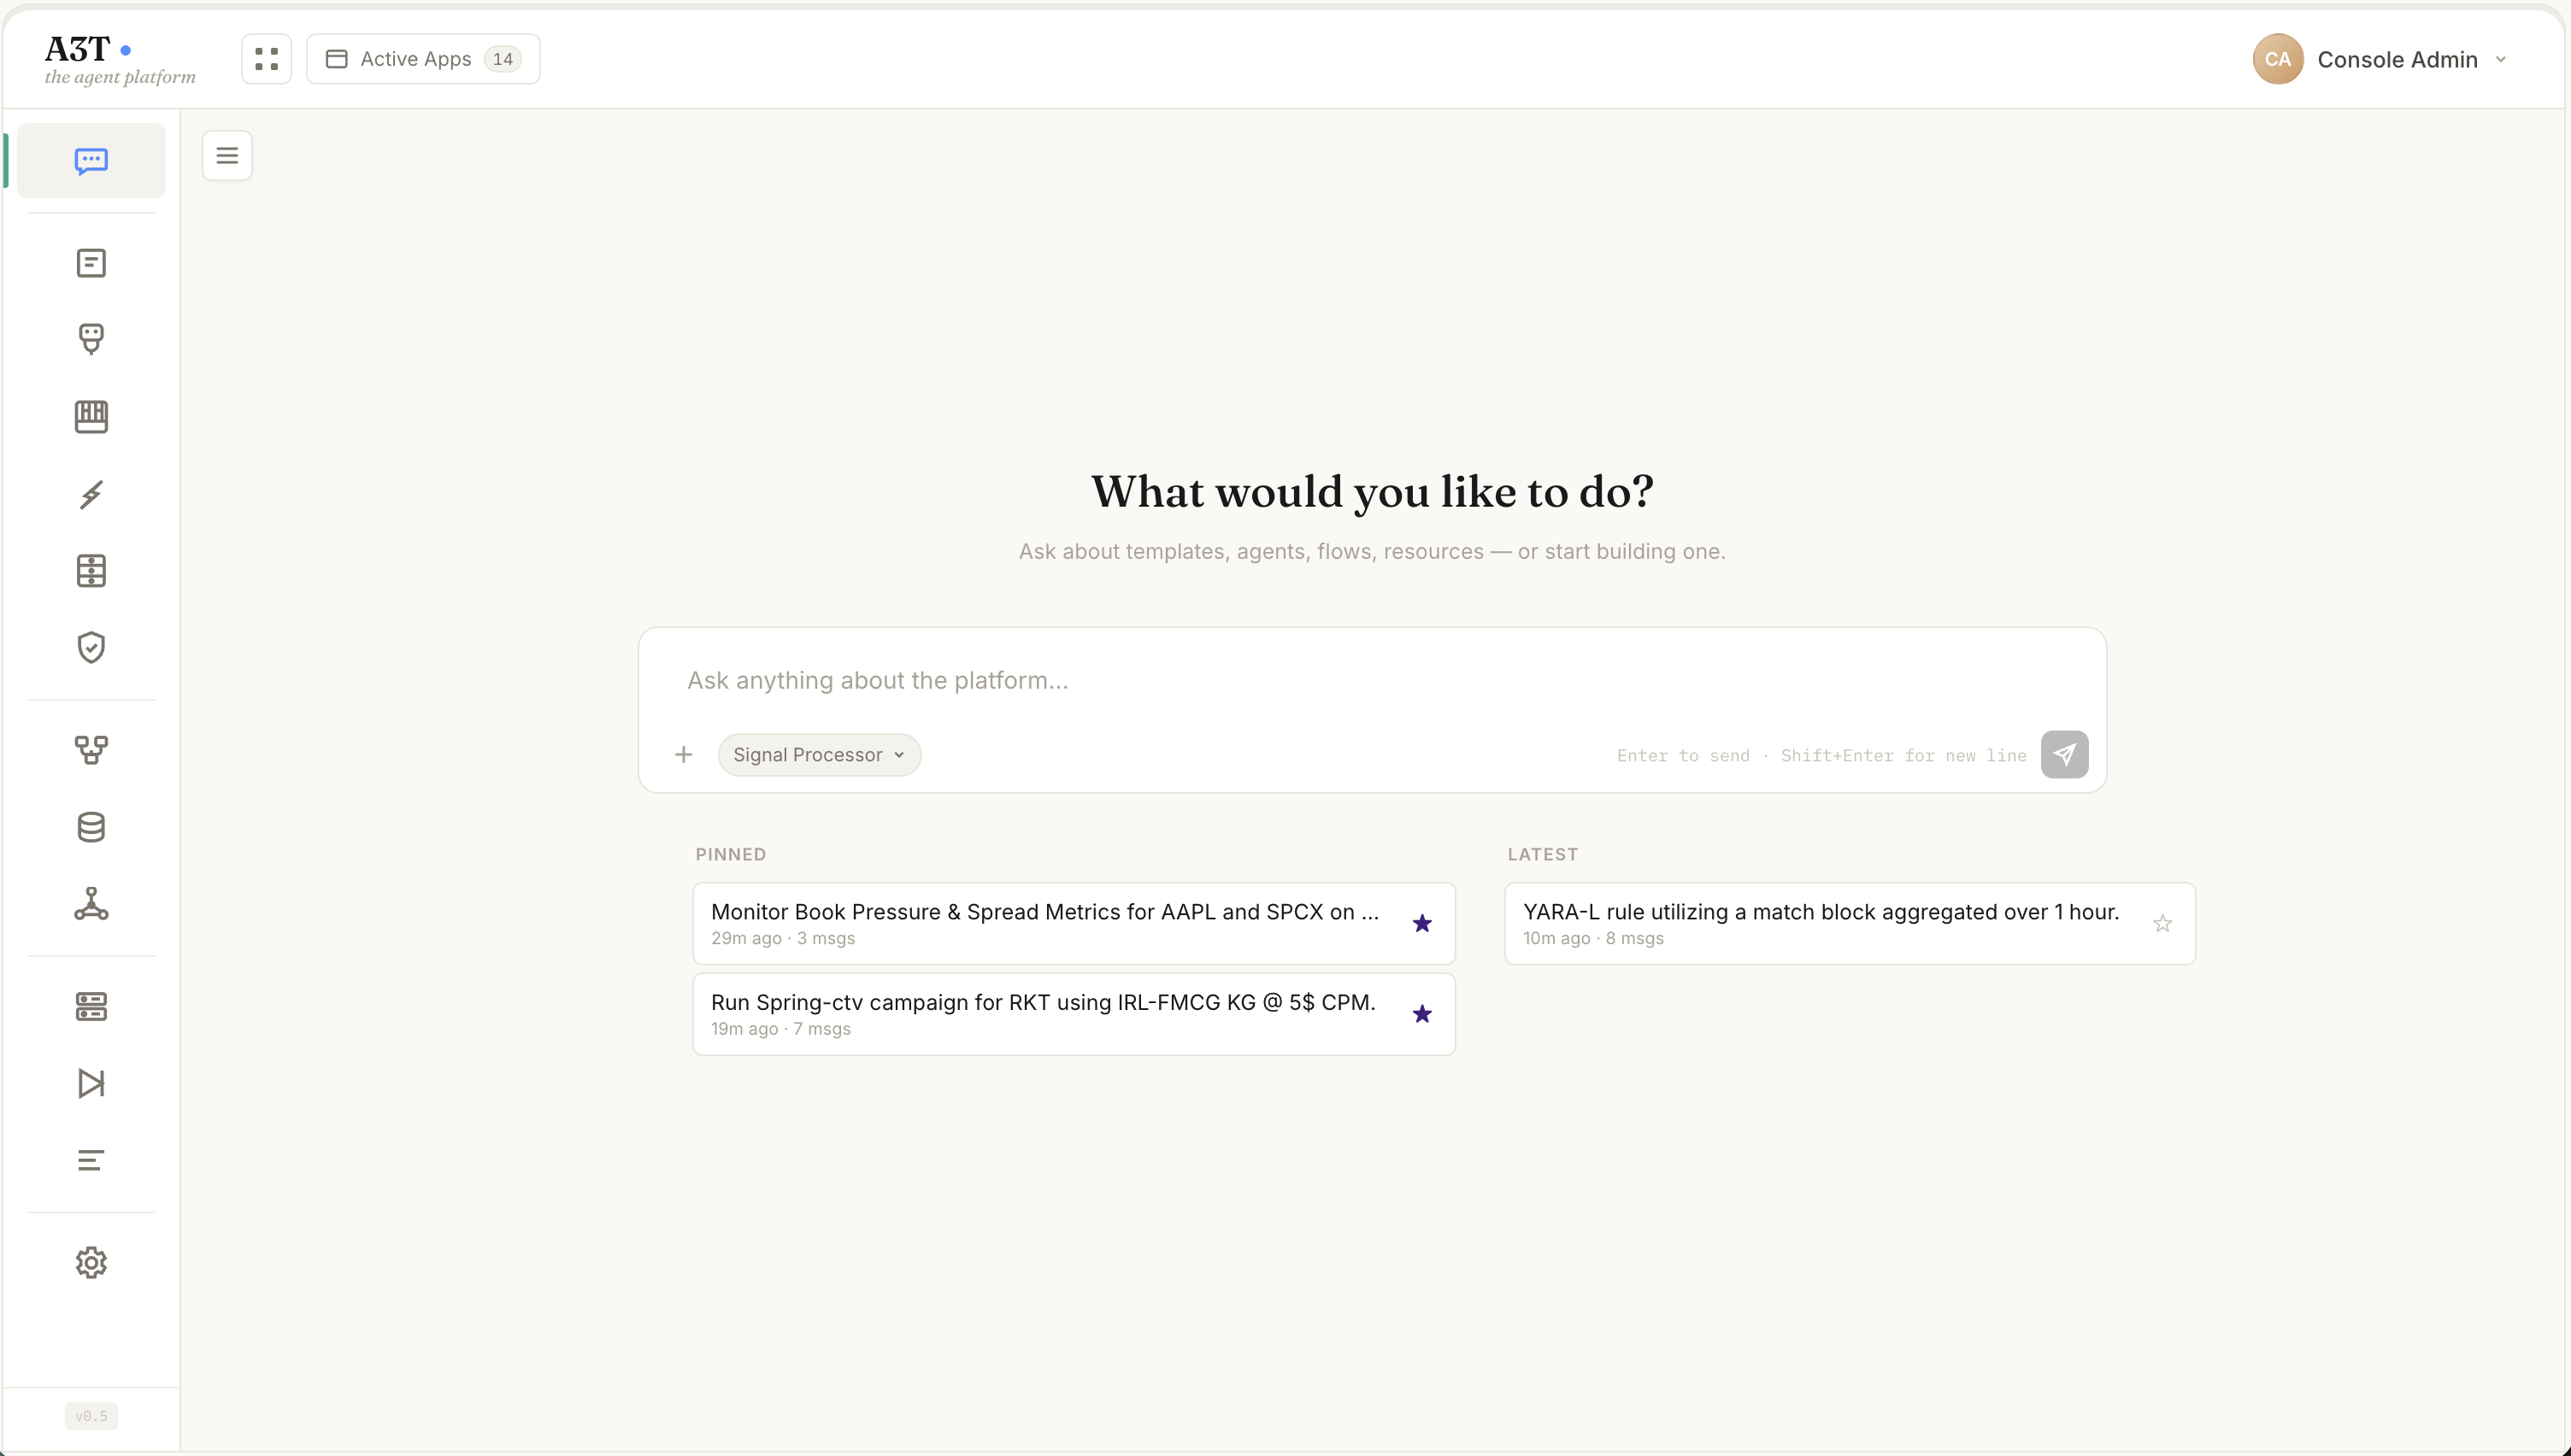
From question to running agent.
Ask the platform. Then build.
The console opens on a conversation. Pick a domain agent — SecOps, Trading, RTB Bidder — and work with it directly, governed by the same policy as everything else.
Templates are CNCF workflows.
Every agent starts as a Serverless Workflow template. Hook flows into lifecycle points — turn start, recall, LLM call, tool call, store, response, turn end — without forking the engine.
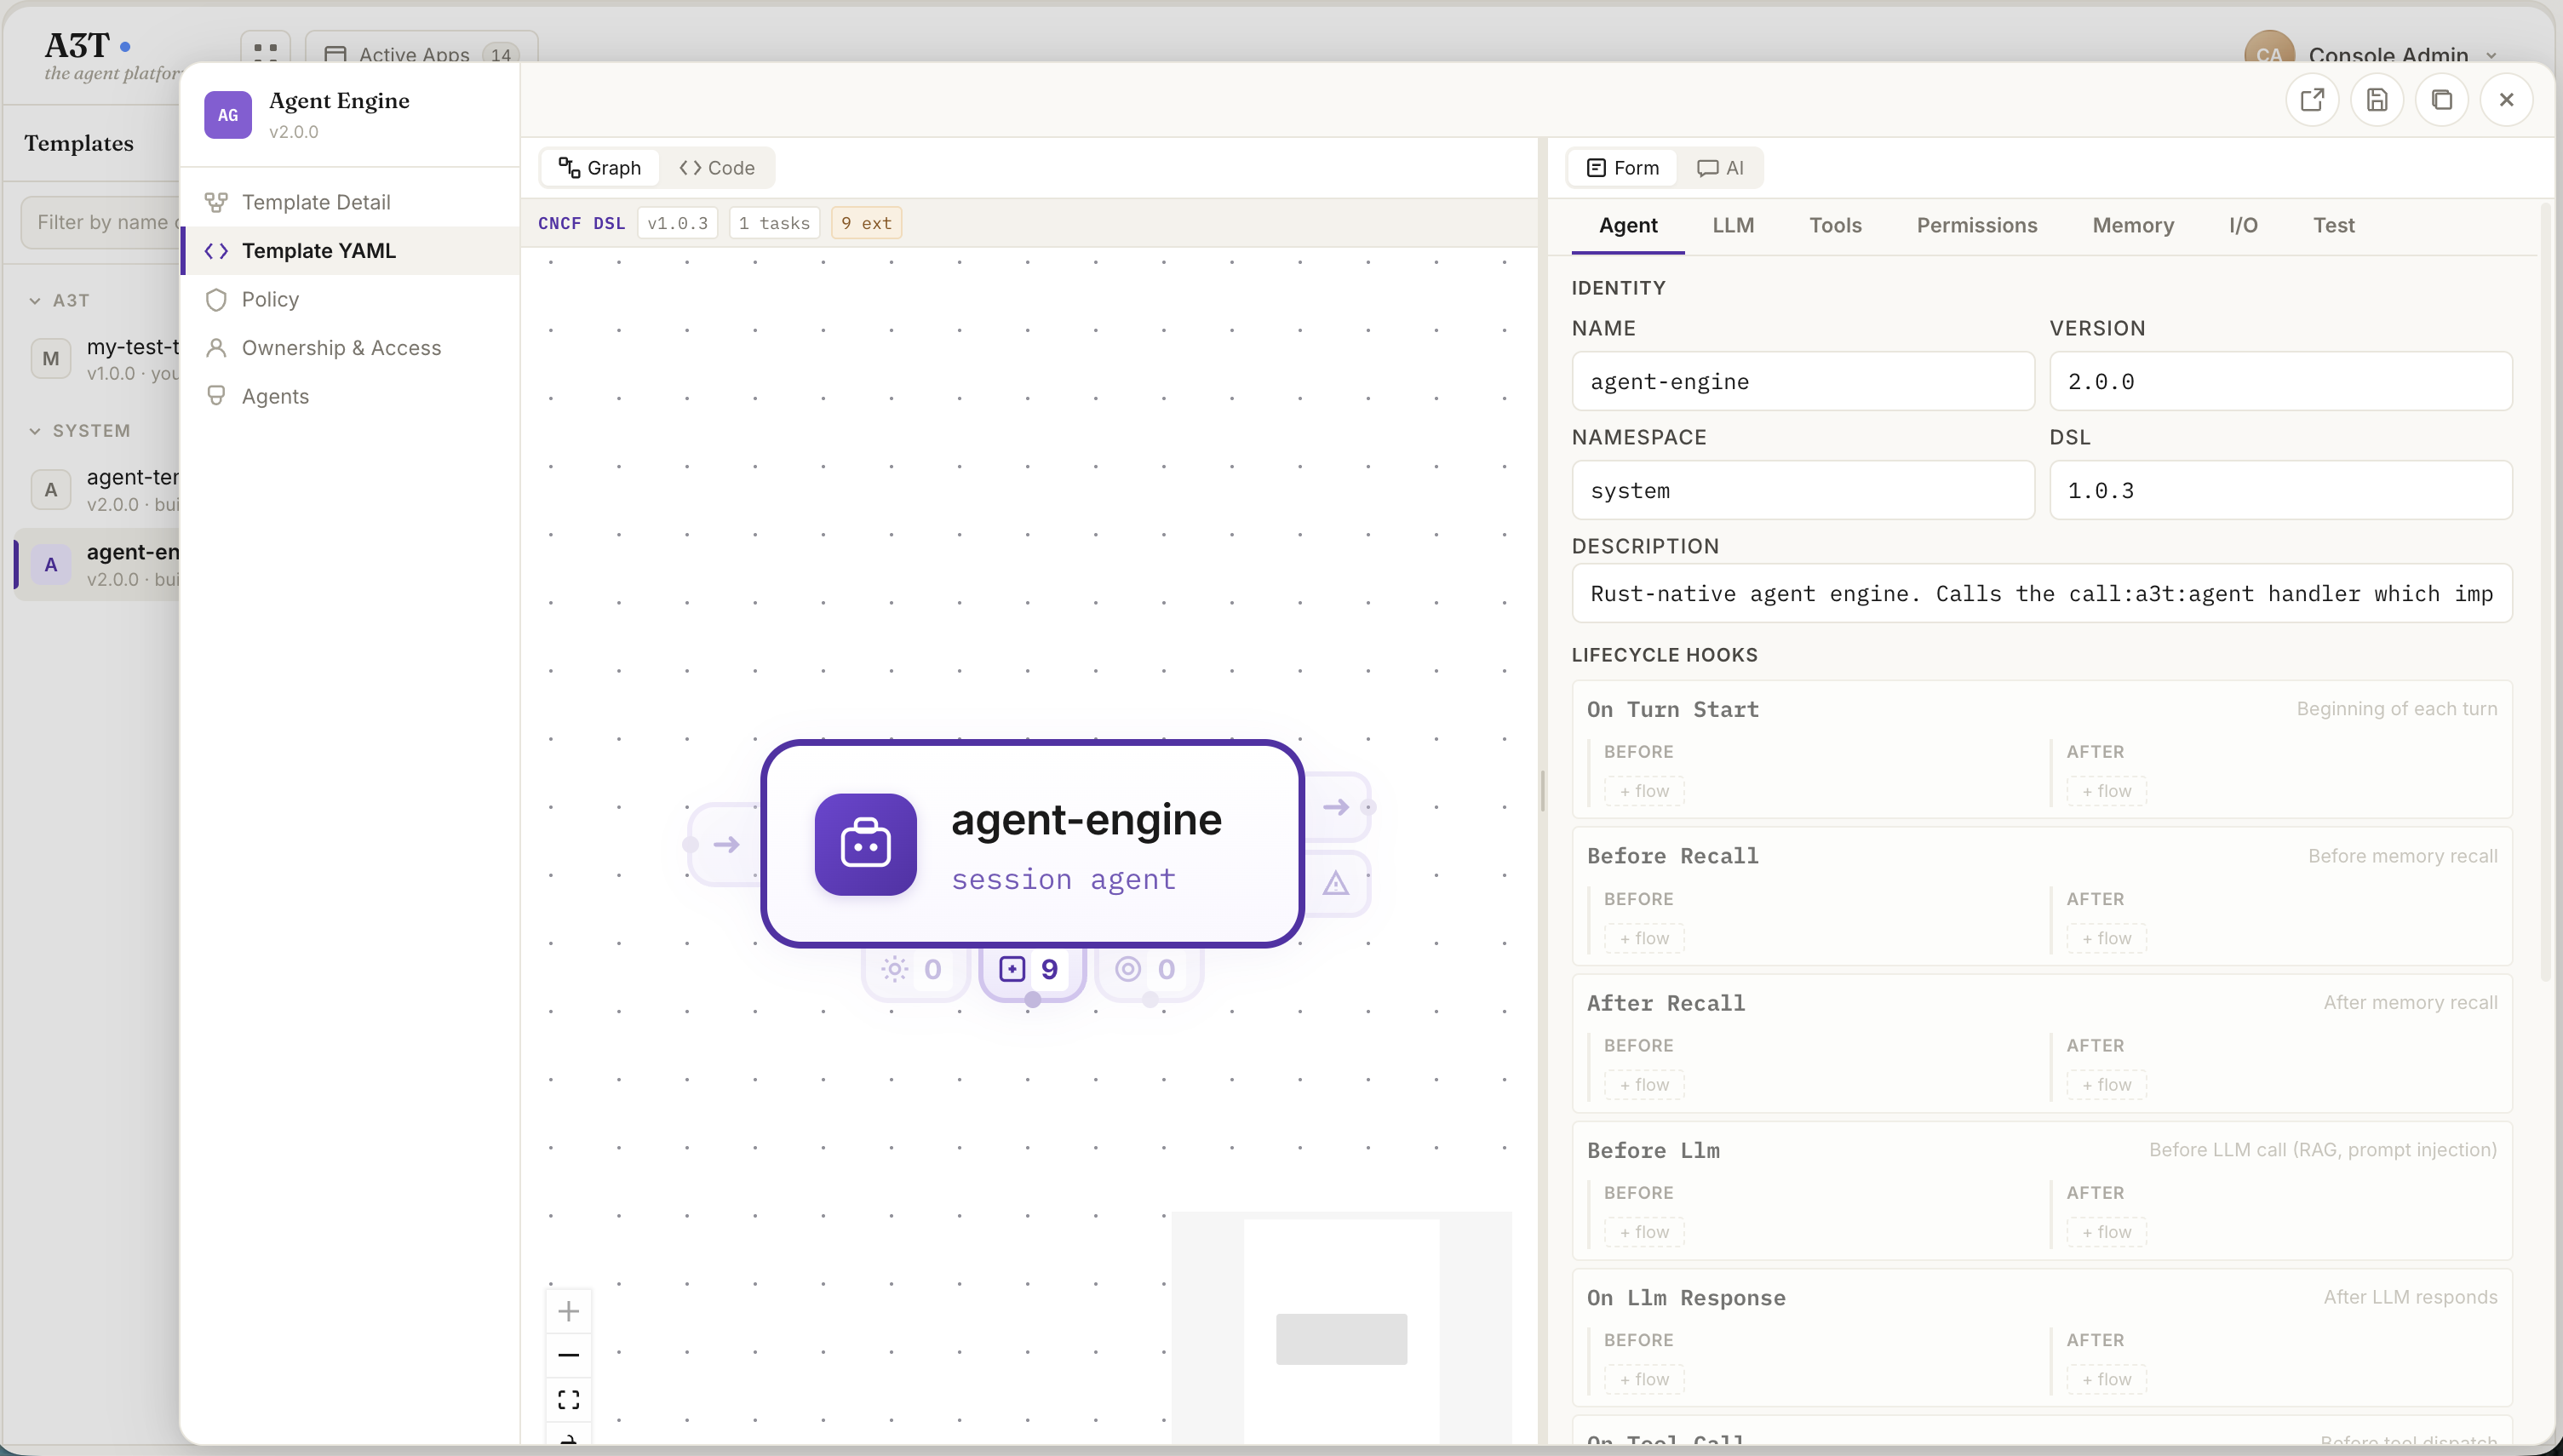
Canvas to code, round-trip.
Flip from Graph to Code and the YAML is the source of truth: diffable, reviewable, and ready for your existing Git workflow. Edit either side; the other follows.
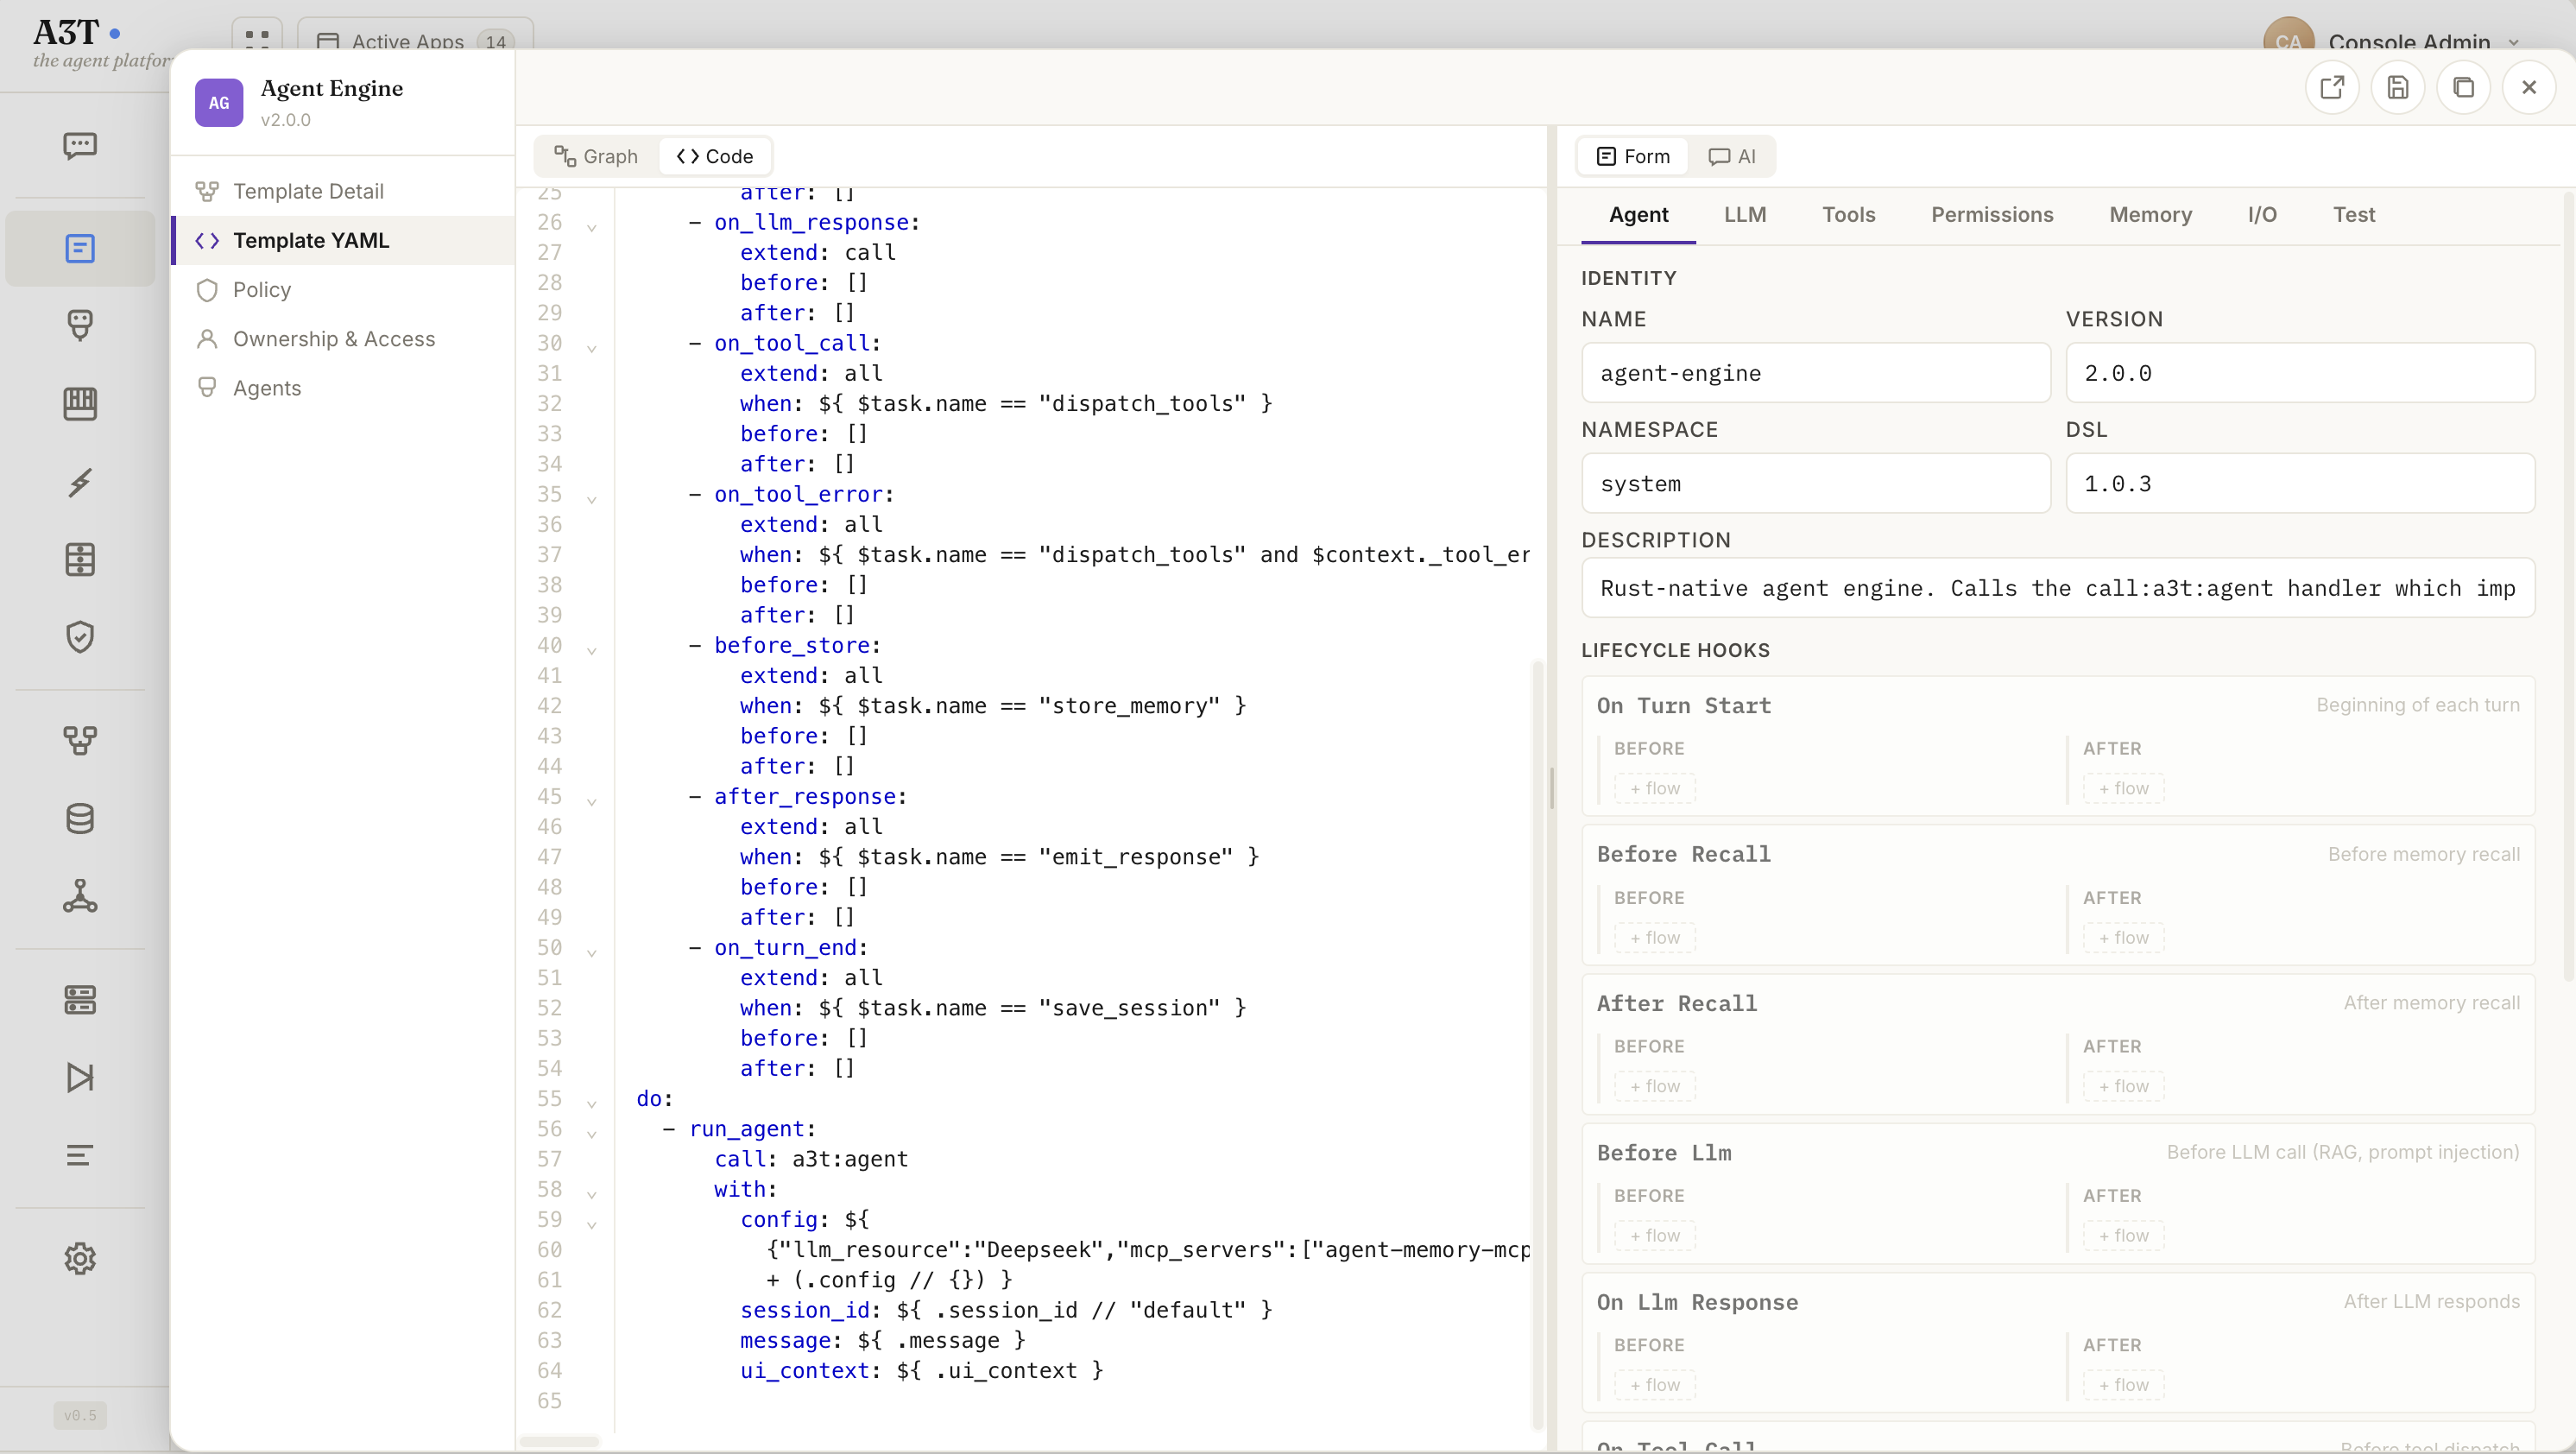
An agent is a template with frozen inputs.
Which LLM to use, which memory store, which MCP servers. Bind a template to resources once, then deploy it to any canvas.
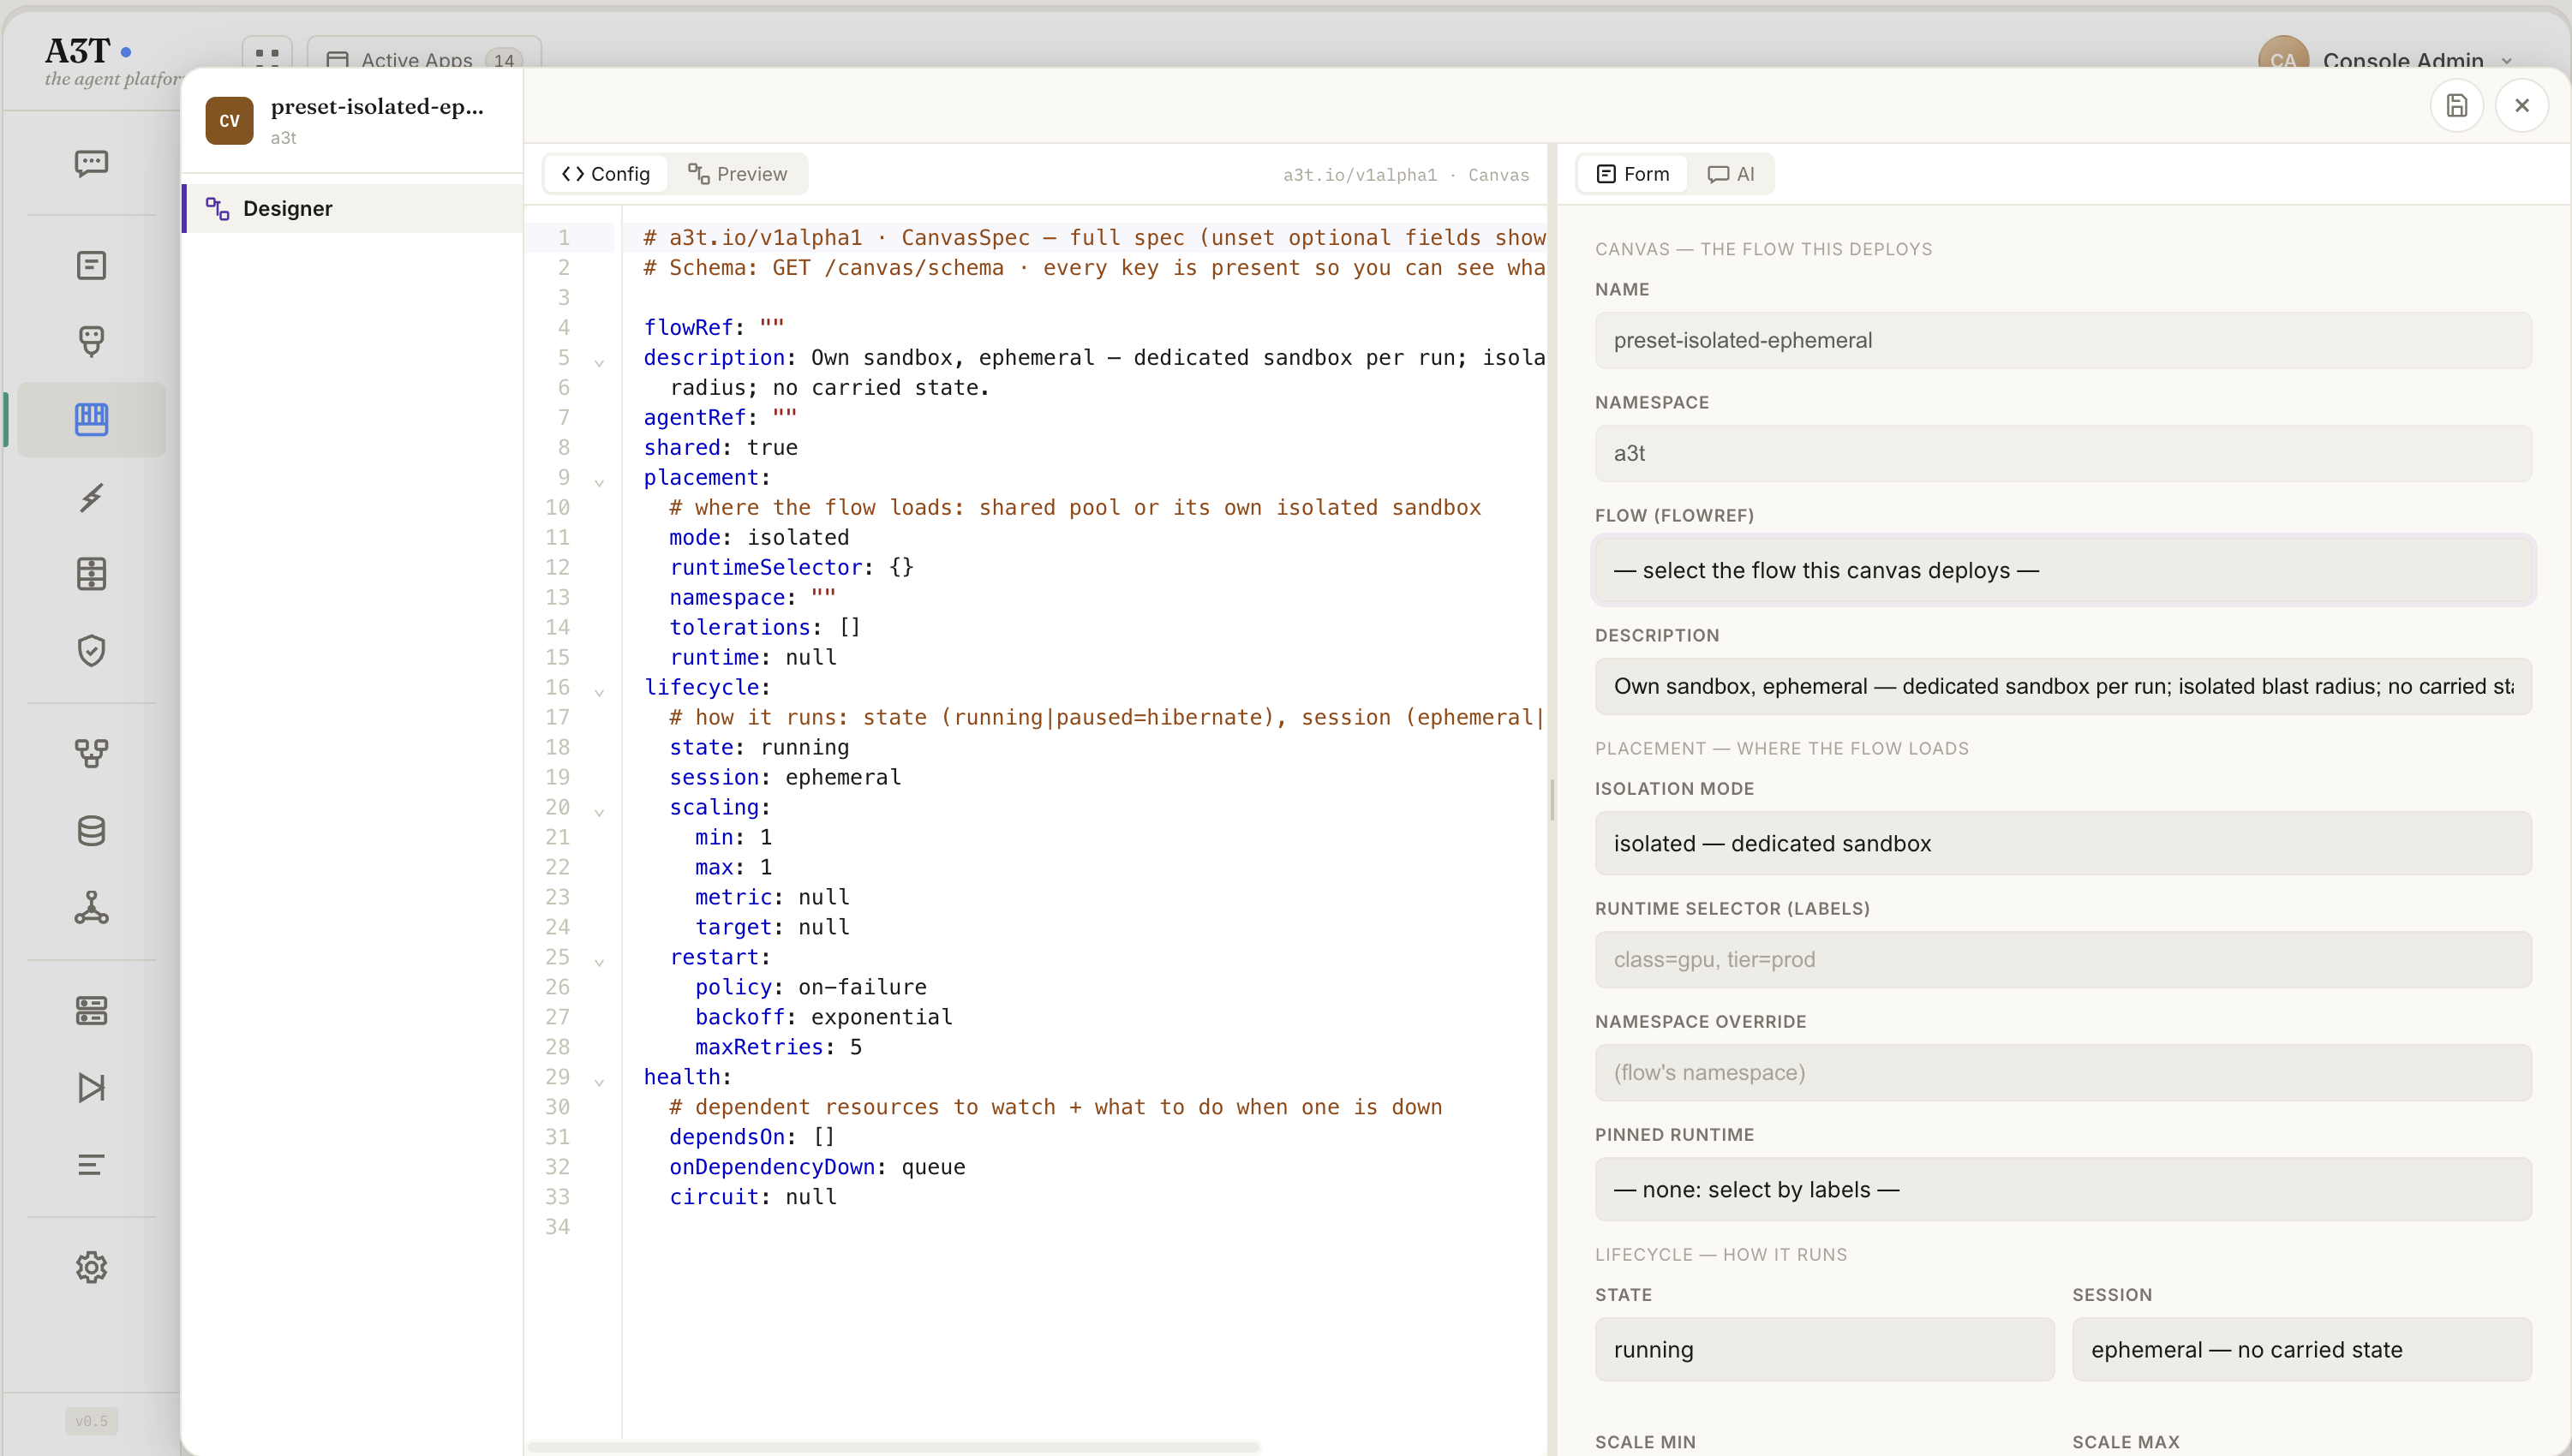
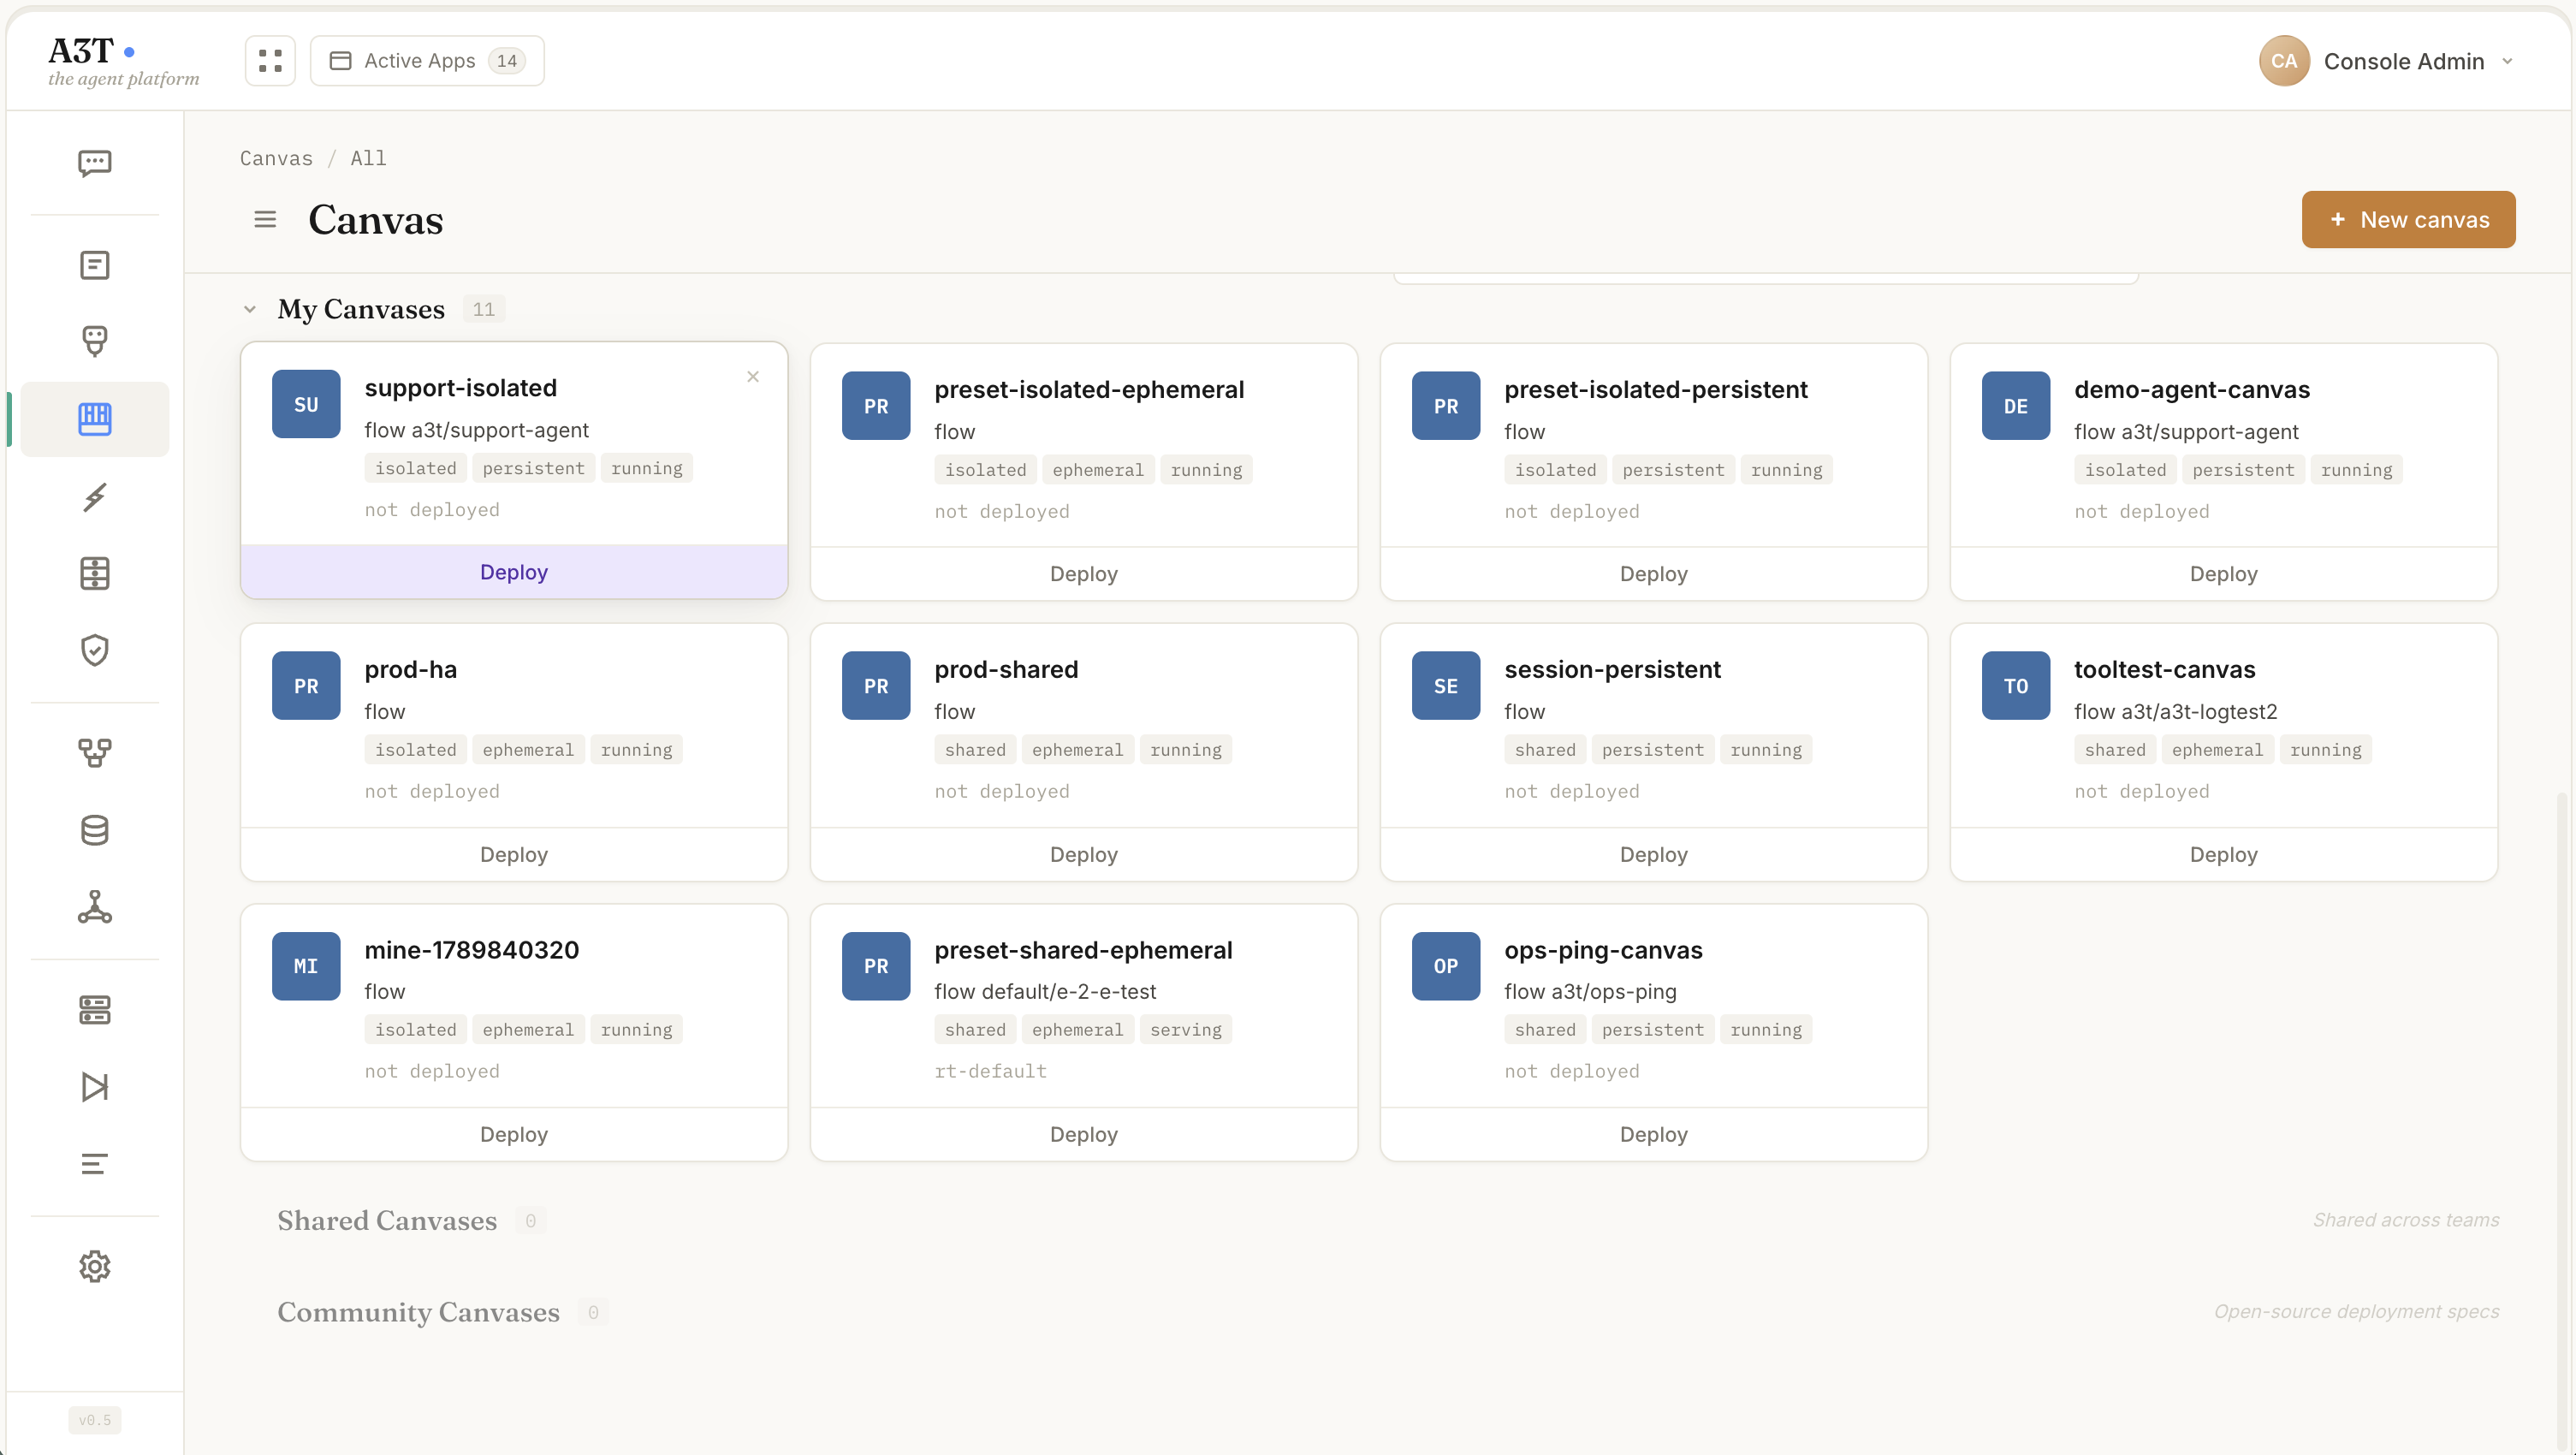
Decide where and how it runs.
A canvas sets placement (shared pool or isolated sandbox), lifecycle (running or hibernated), sessions (ephemeral or persistent), scaling, restart policy and dependency health — as a form or as YAML.
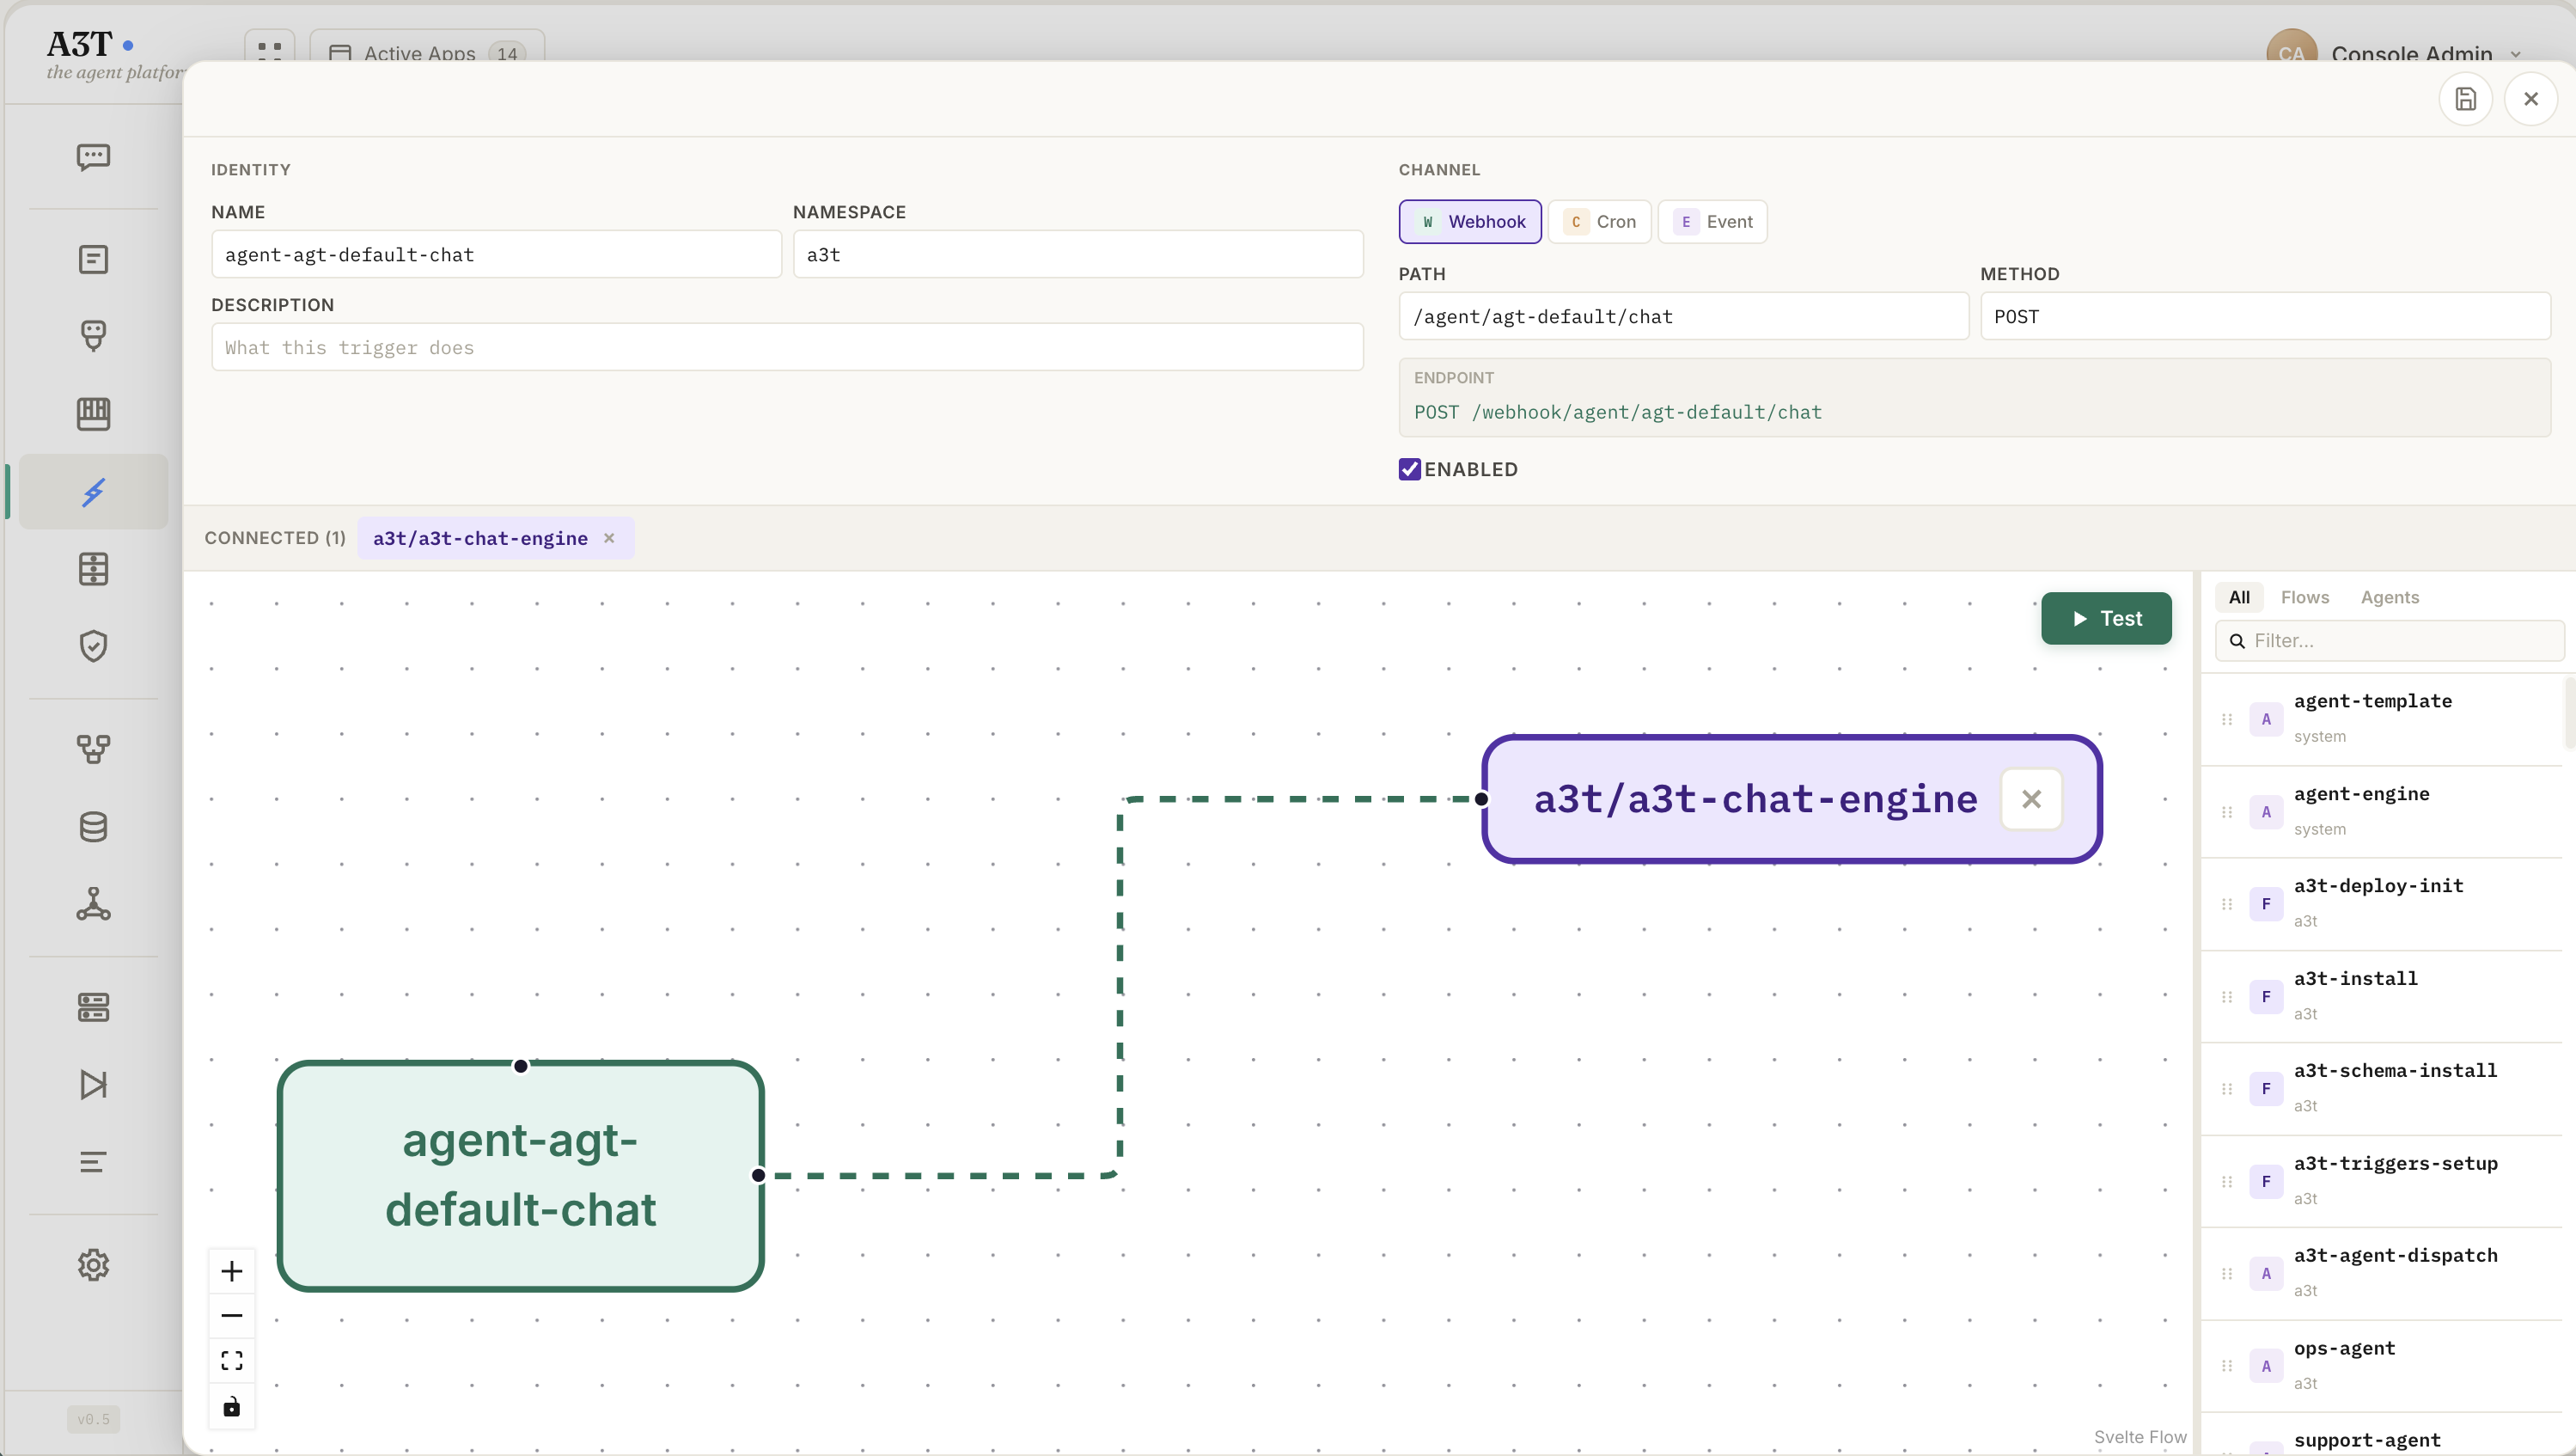
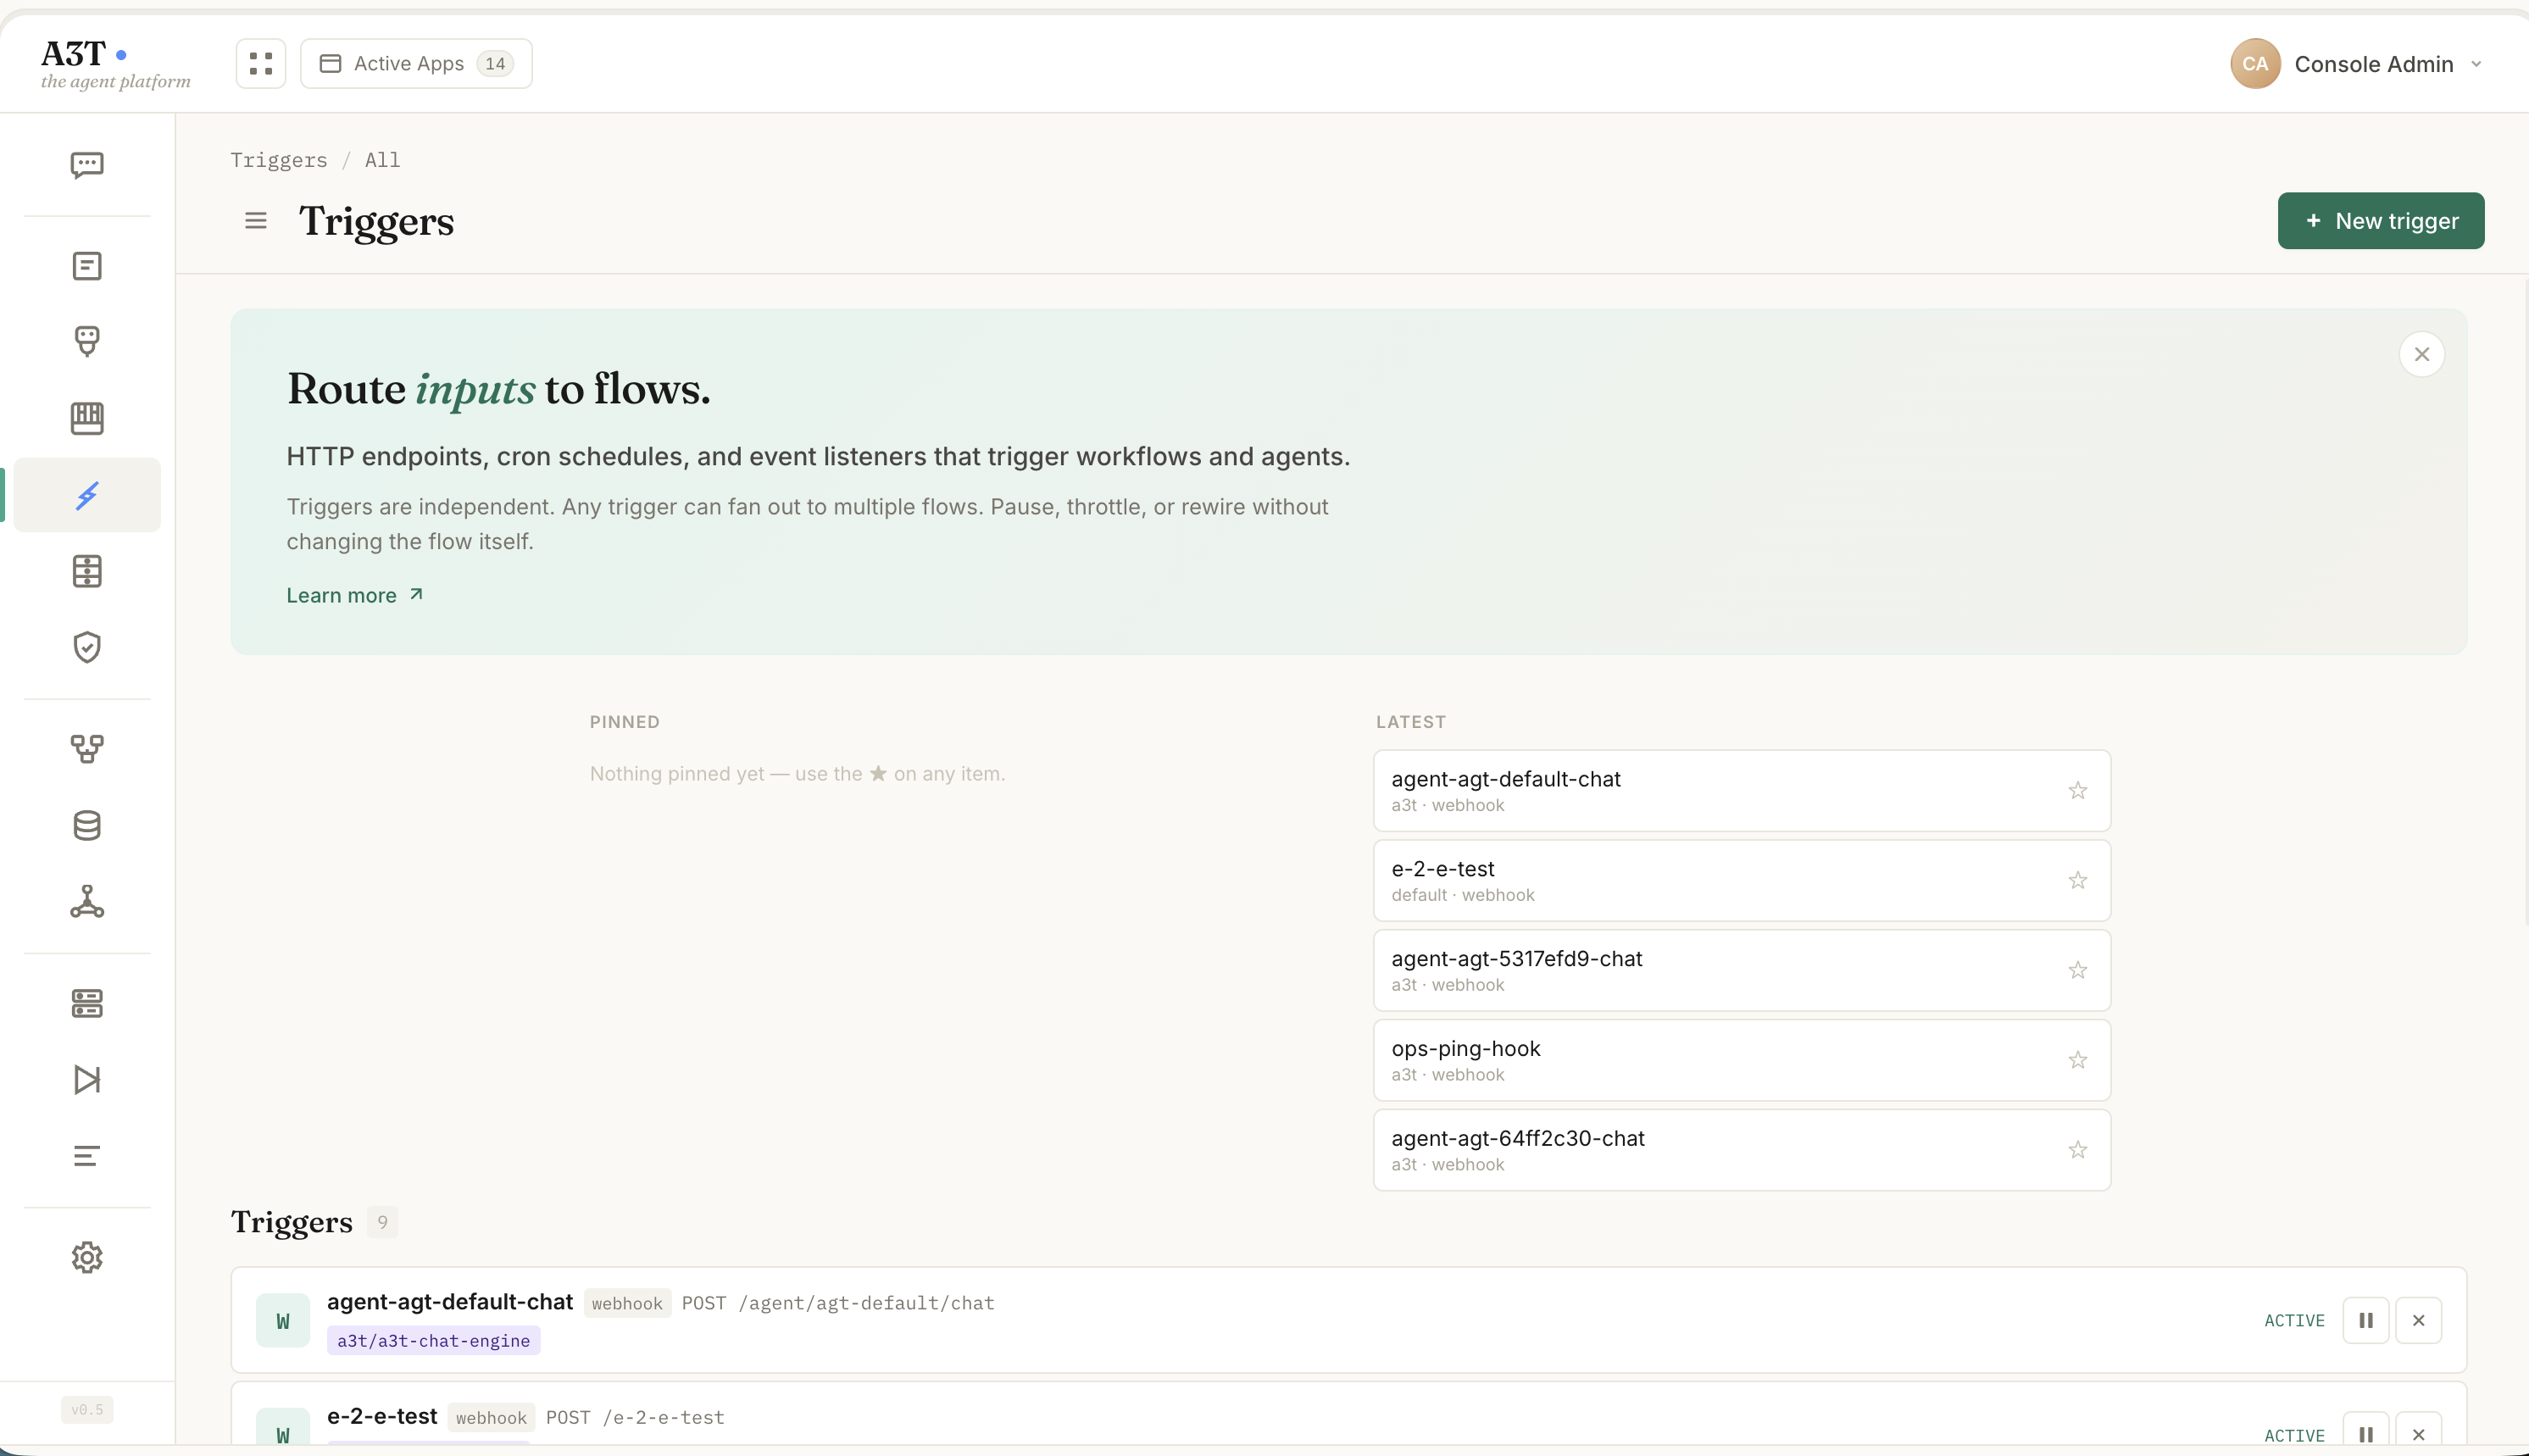
Route inputs to flows.
Webhooks, cron schedules and event listeners. Any trigger can fan out to multiple flows — pause, throttle or rewire without changing the flow itself.
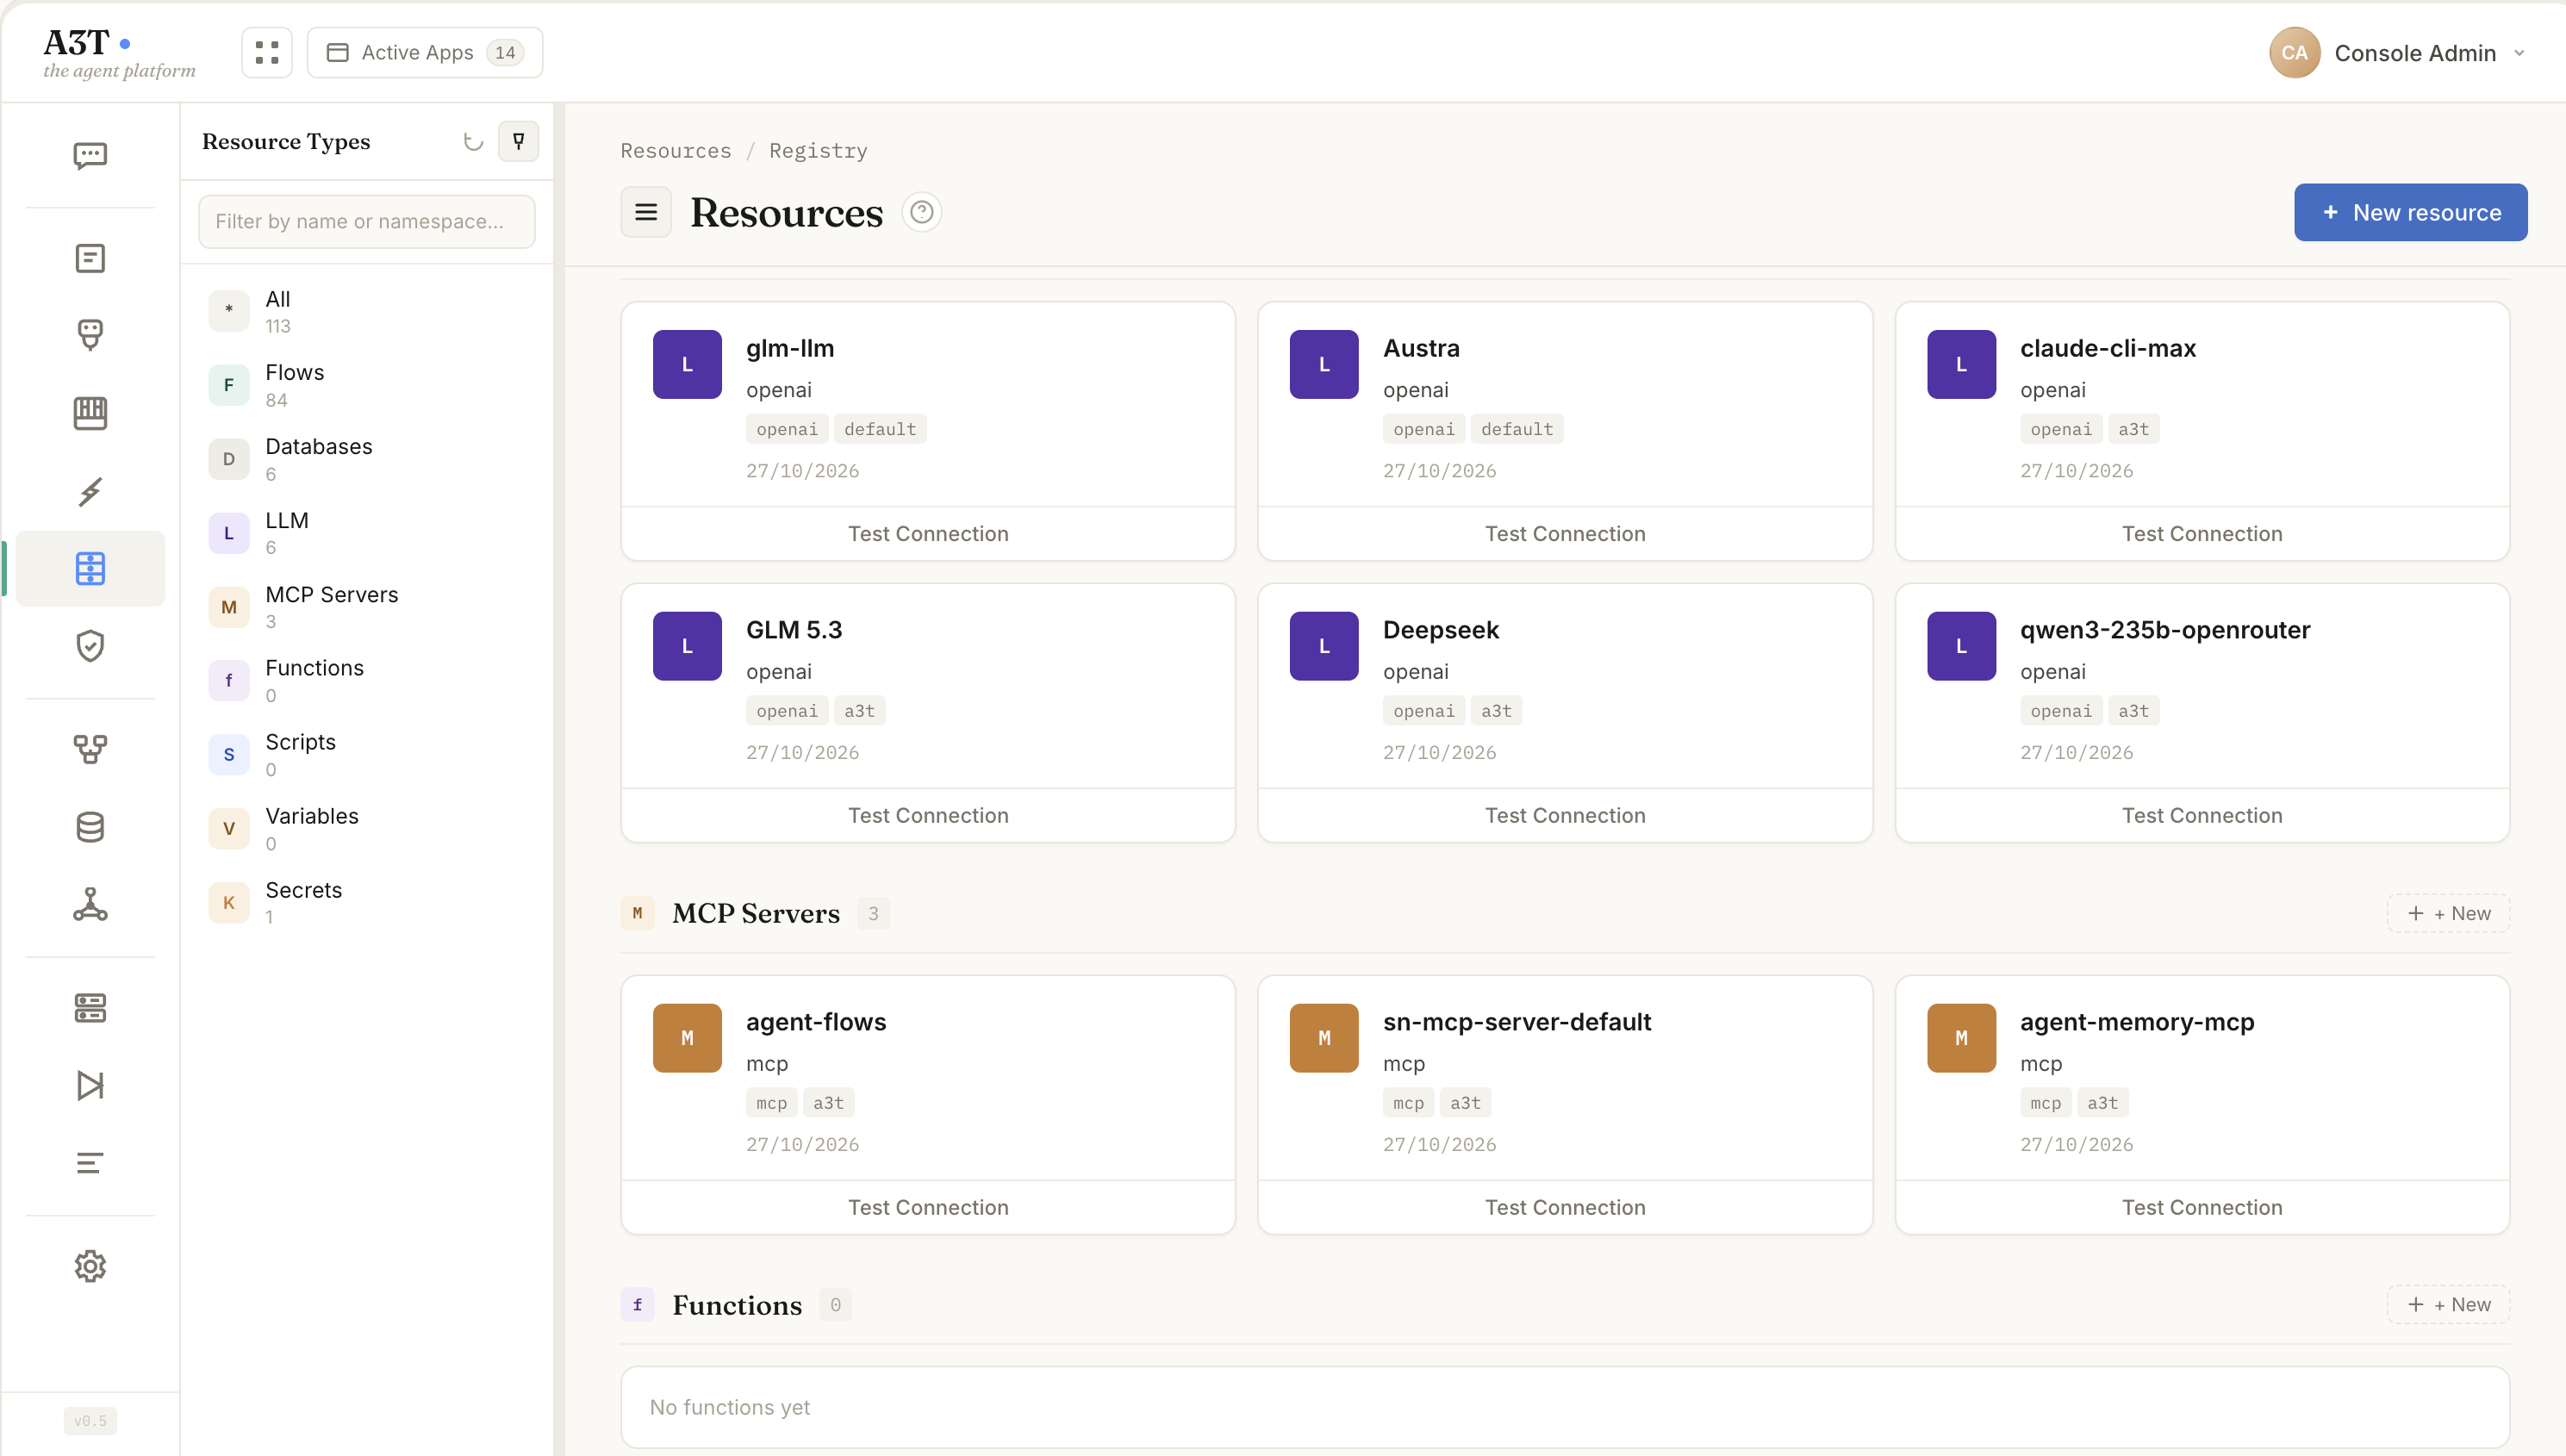
Name your dependencies once.
LLMs, MCP servers, databases, functions, variables and secrets are namespaced resources. Test the connection, then reference them by name from any flow or agent.
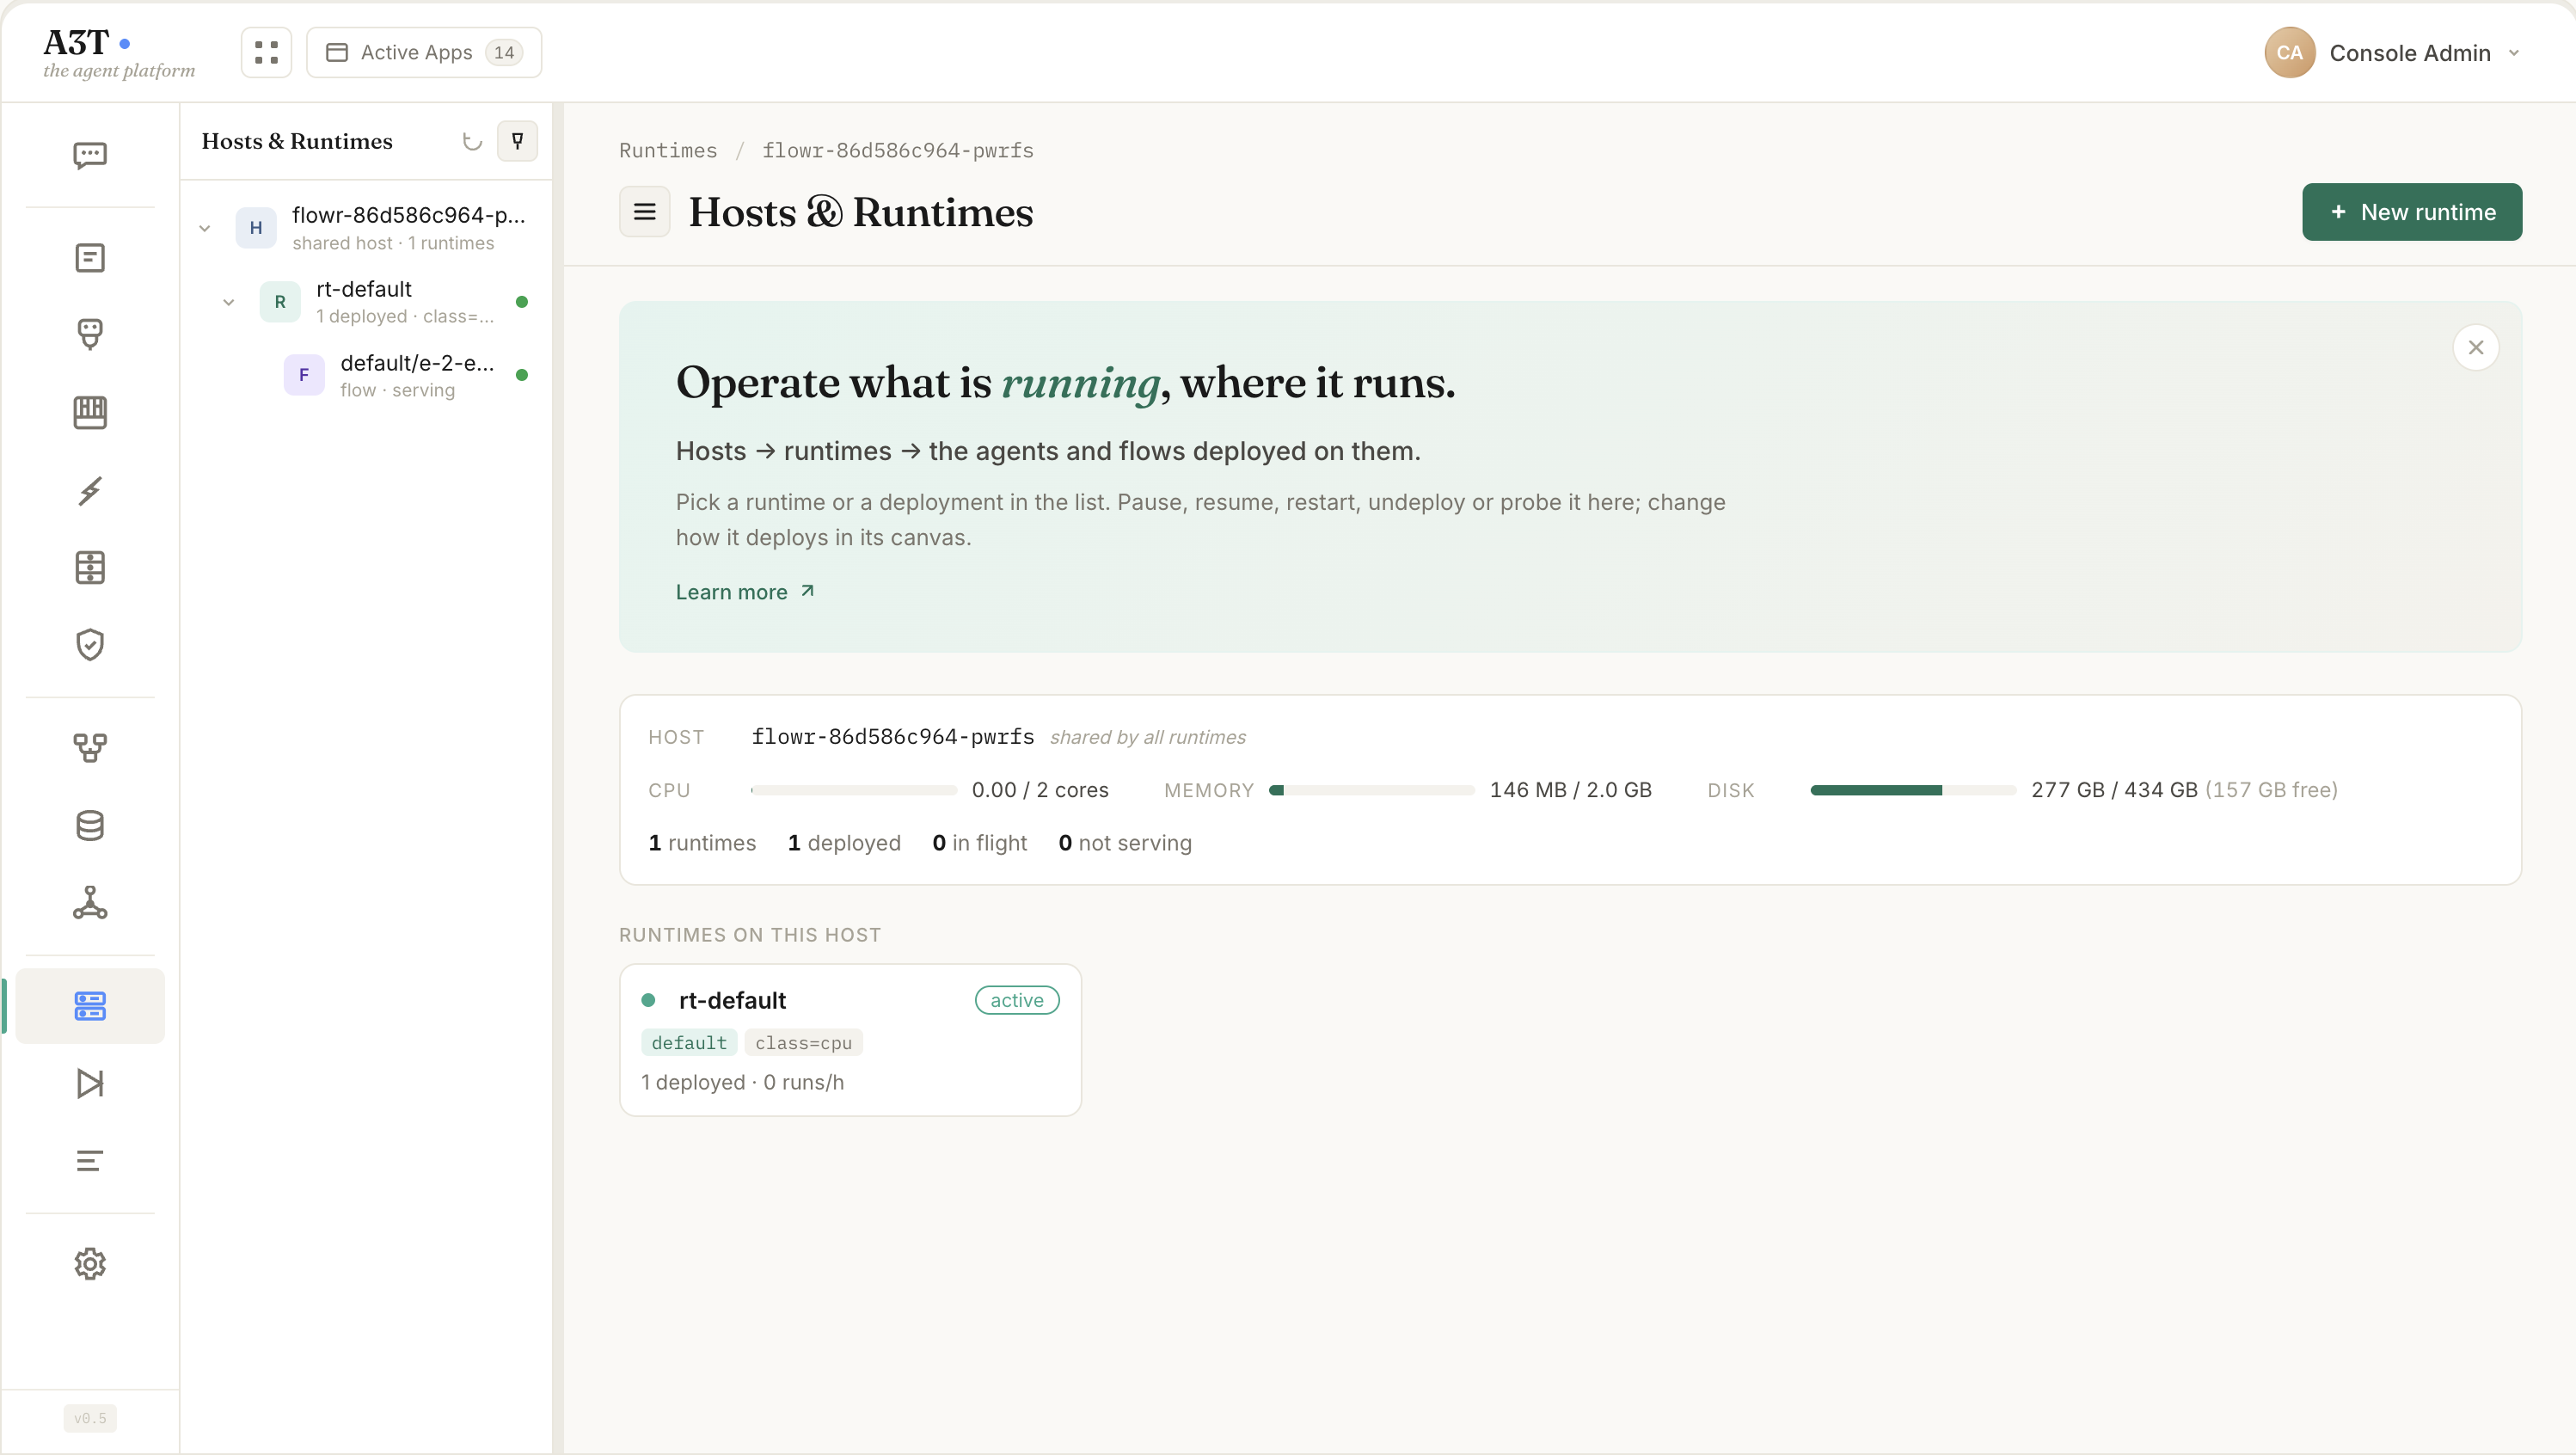
Operate what is running, where it runs.
Hosts → runtimes → the agents and flows deployed on them. Pause, resume, restart, undeploy or probe — with capacity and health on one screen.
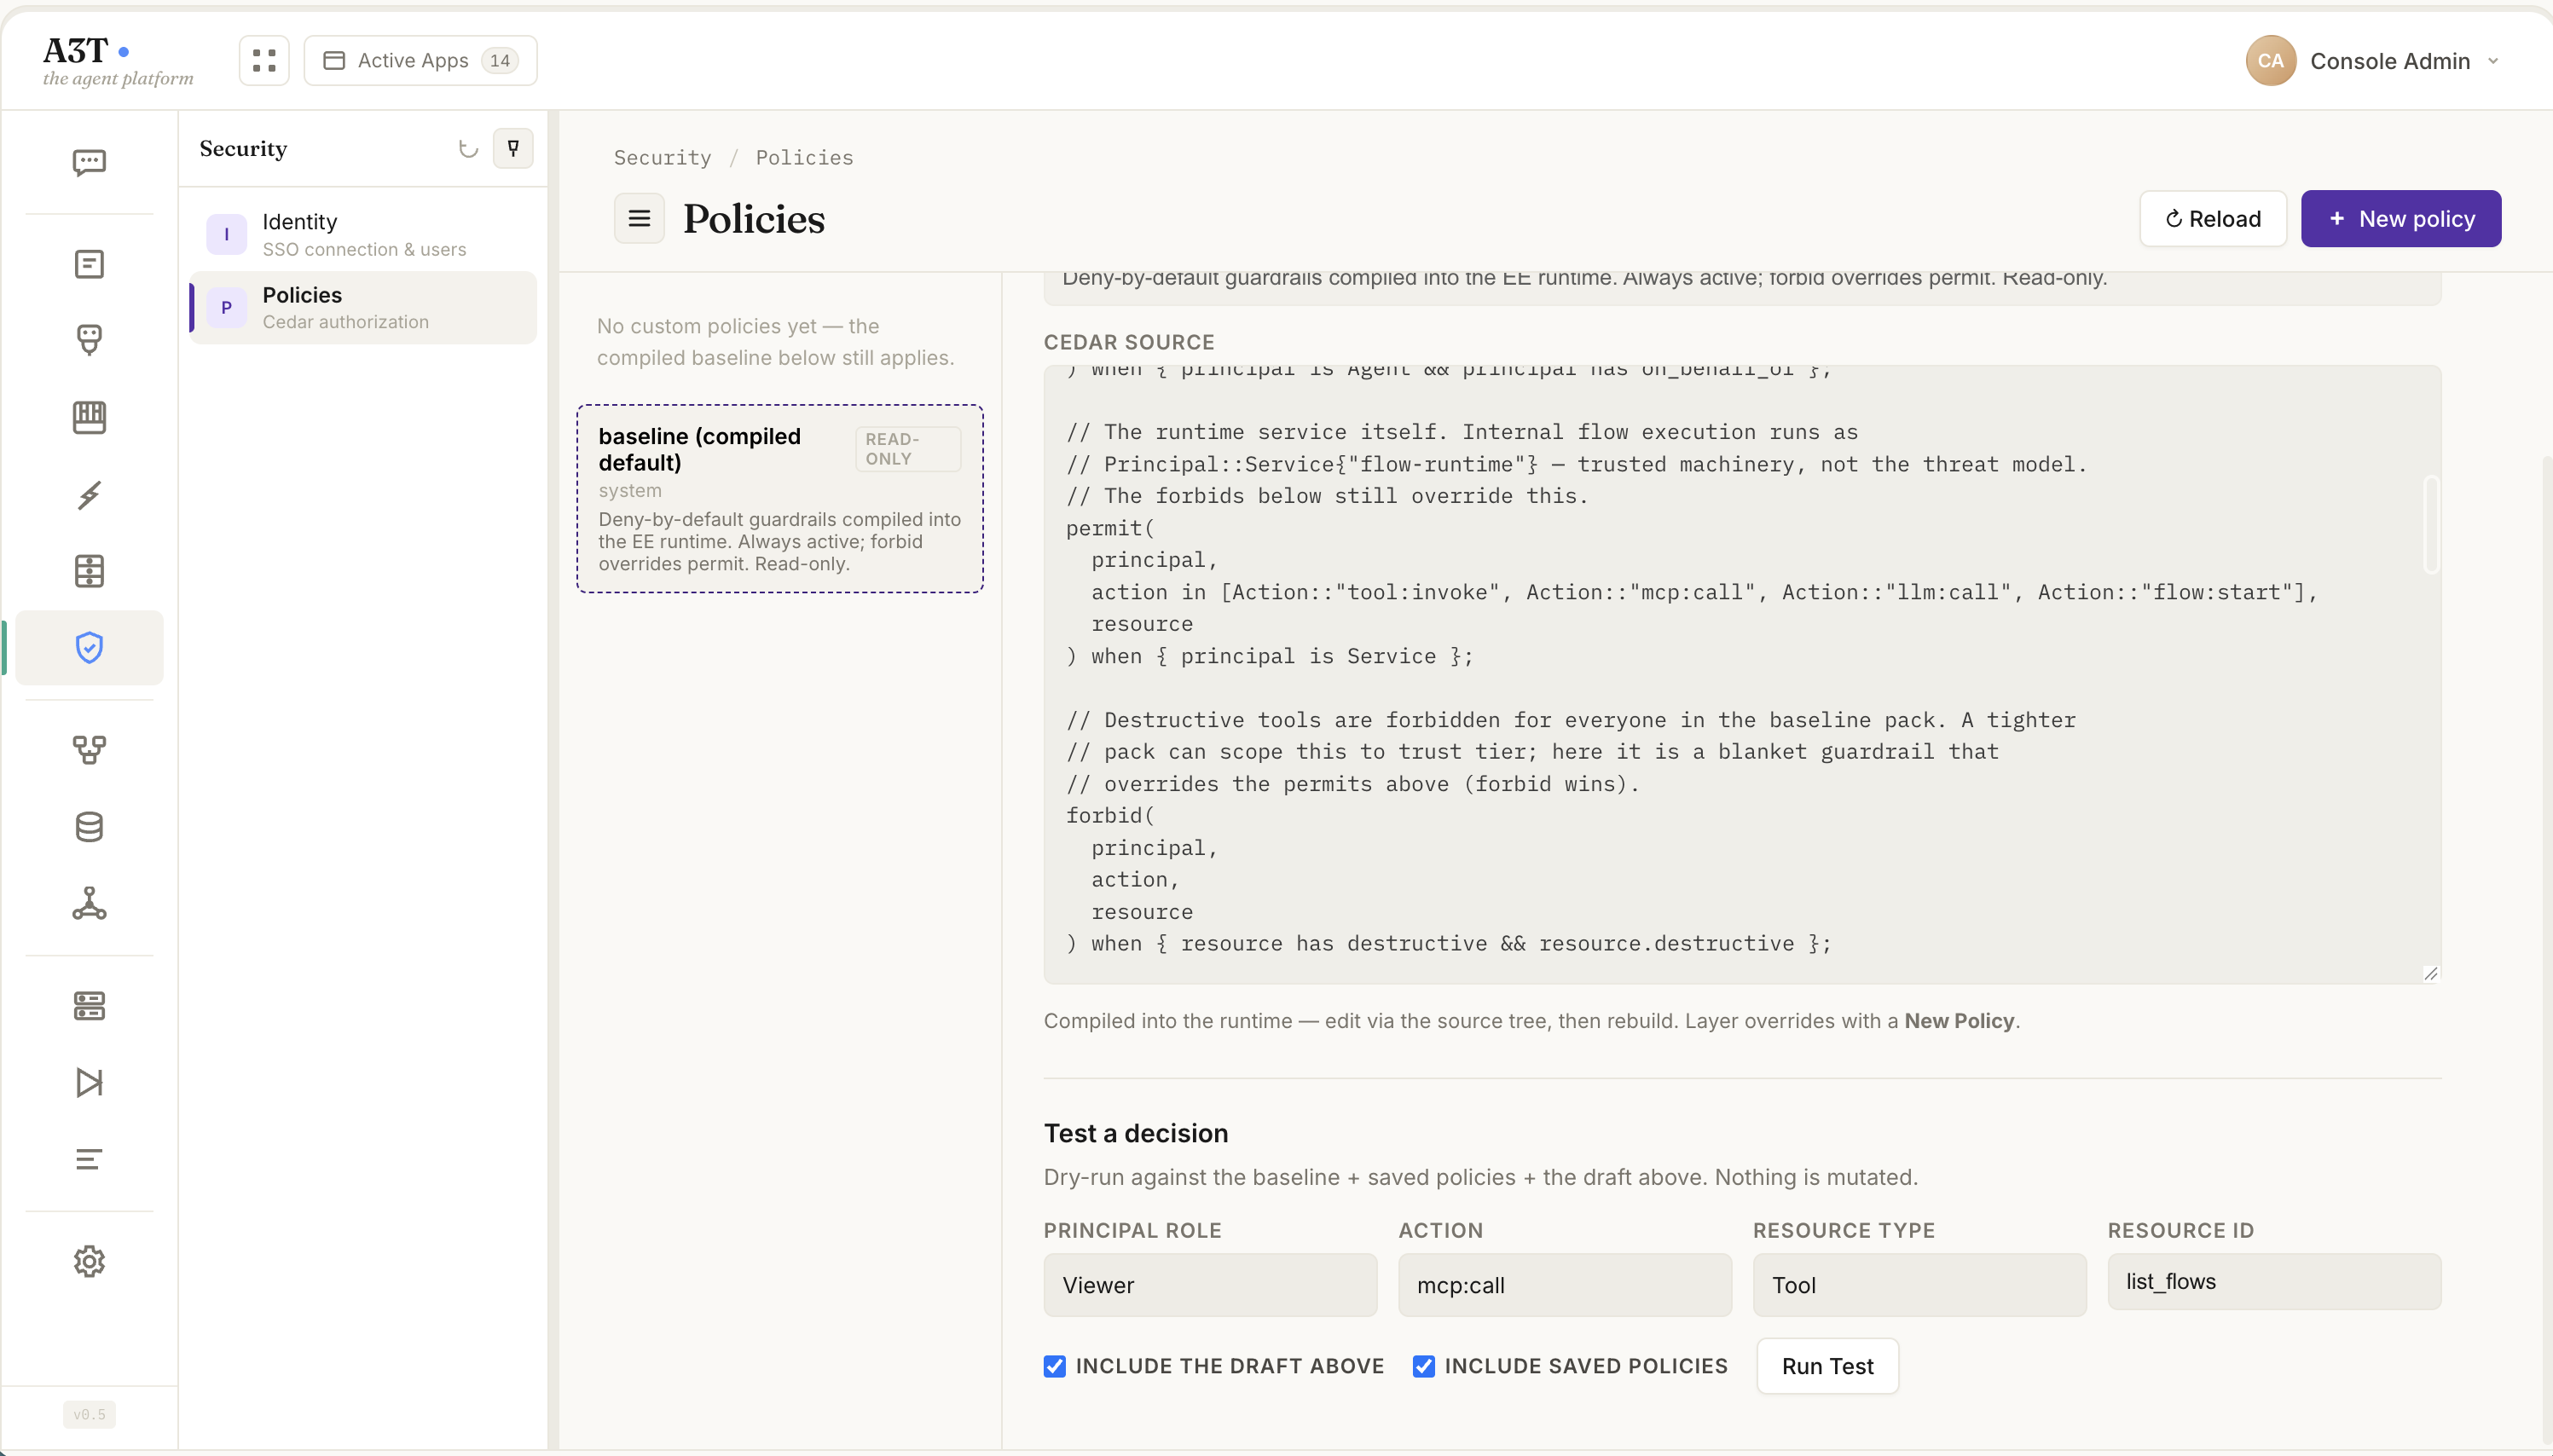
Every decision, on the record.
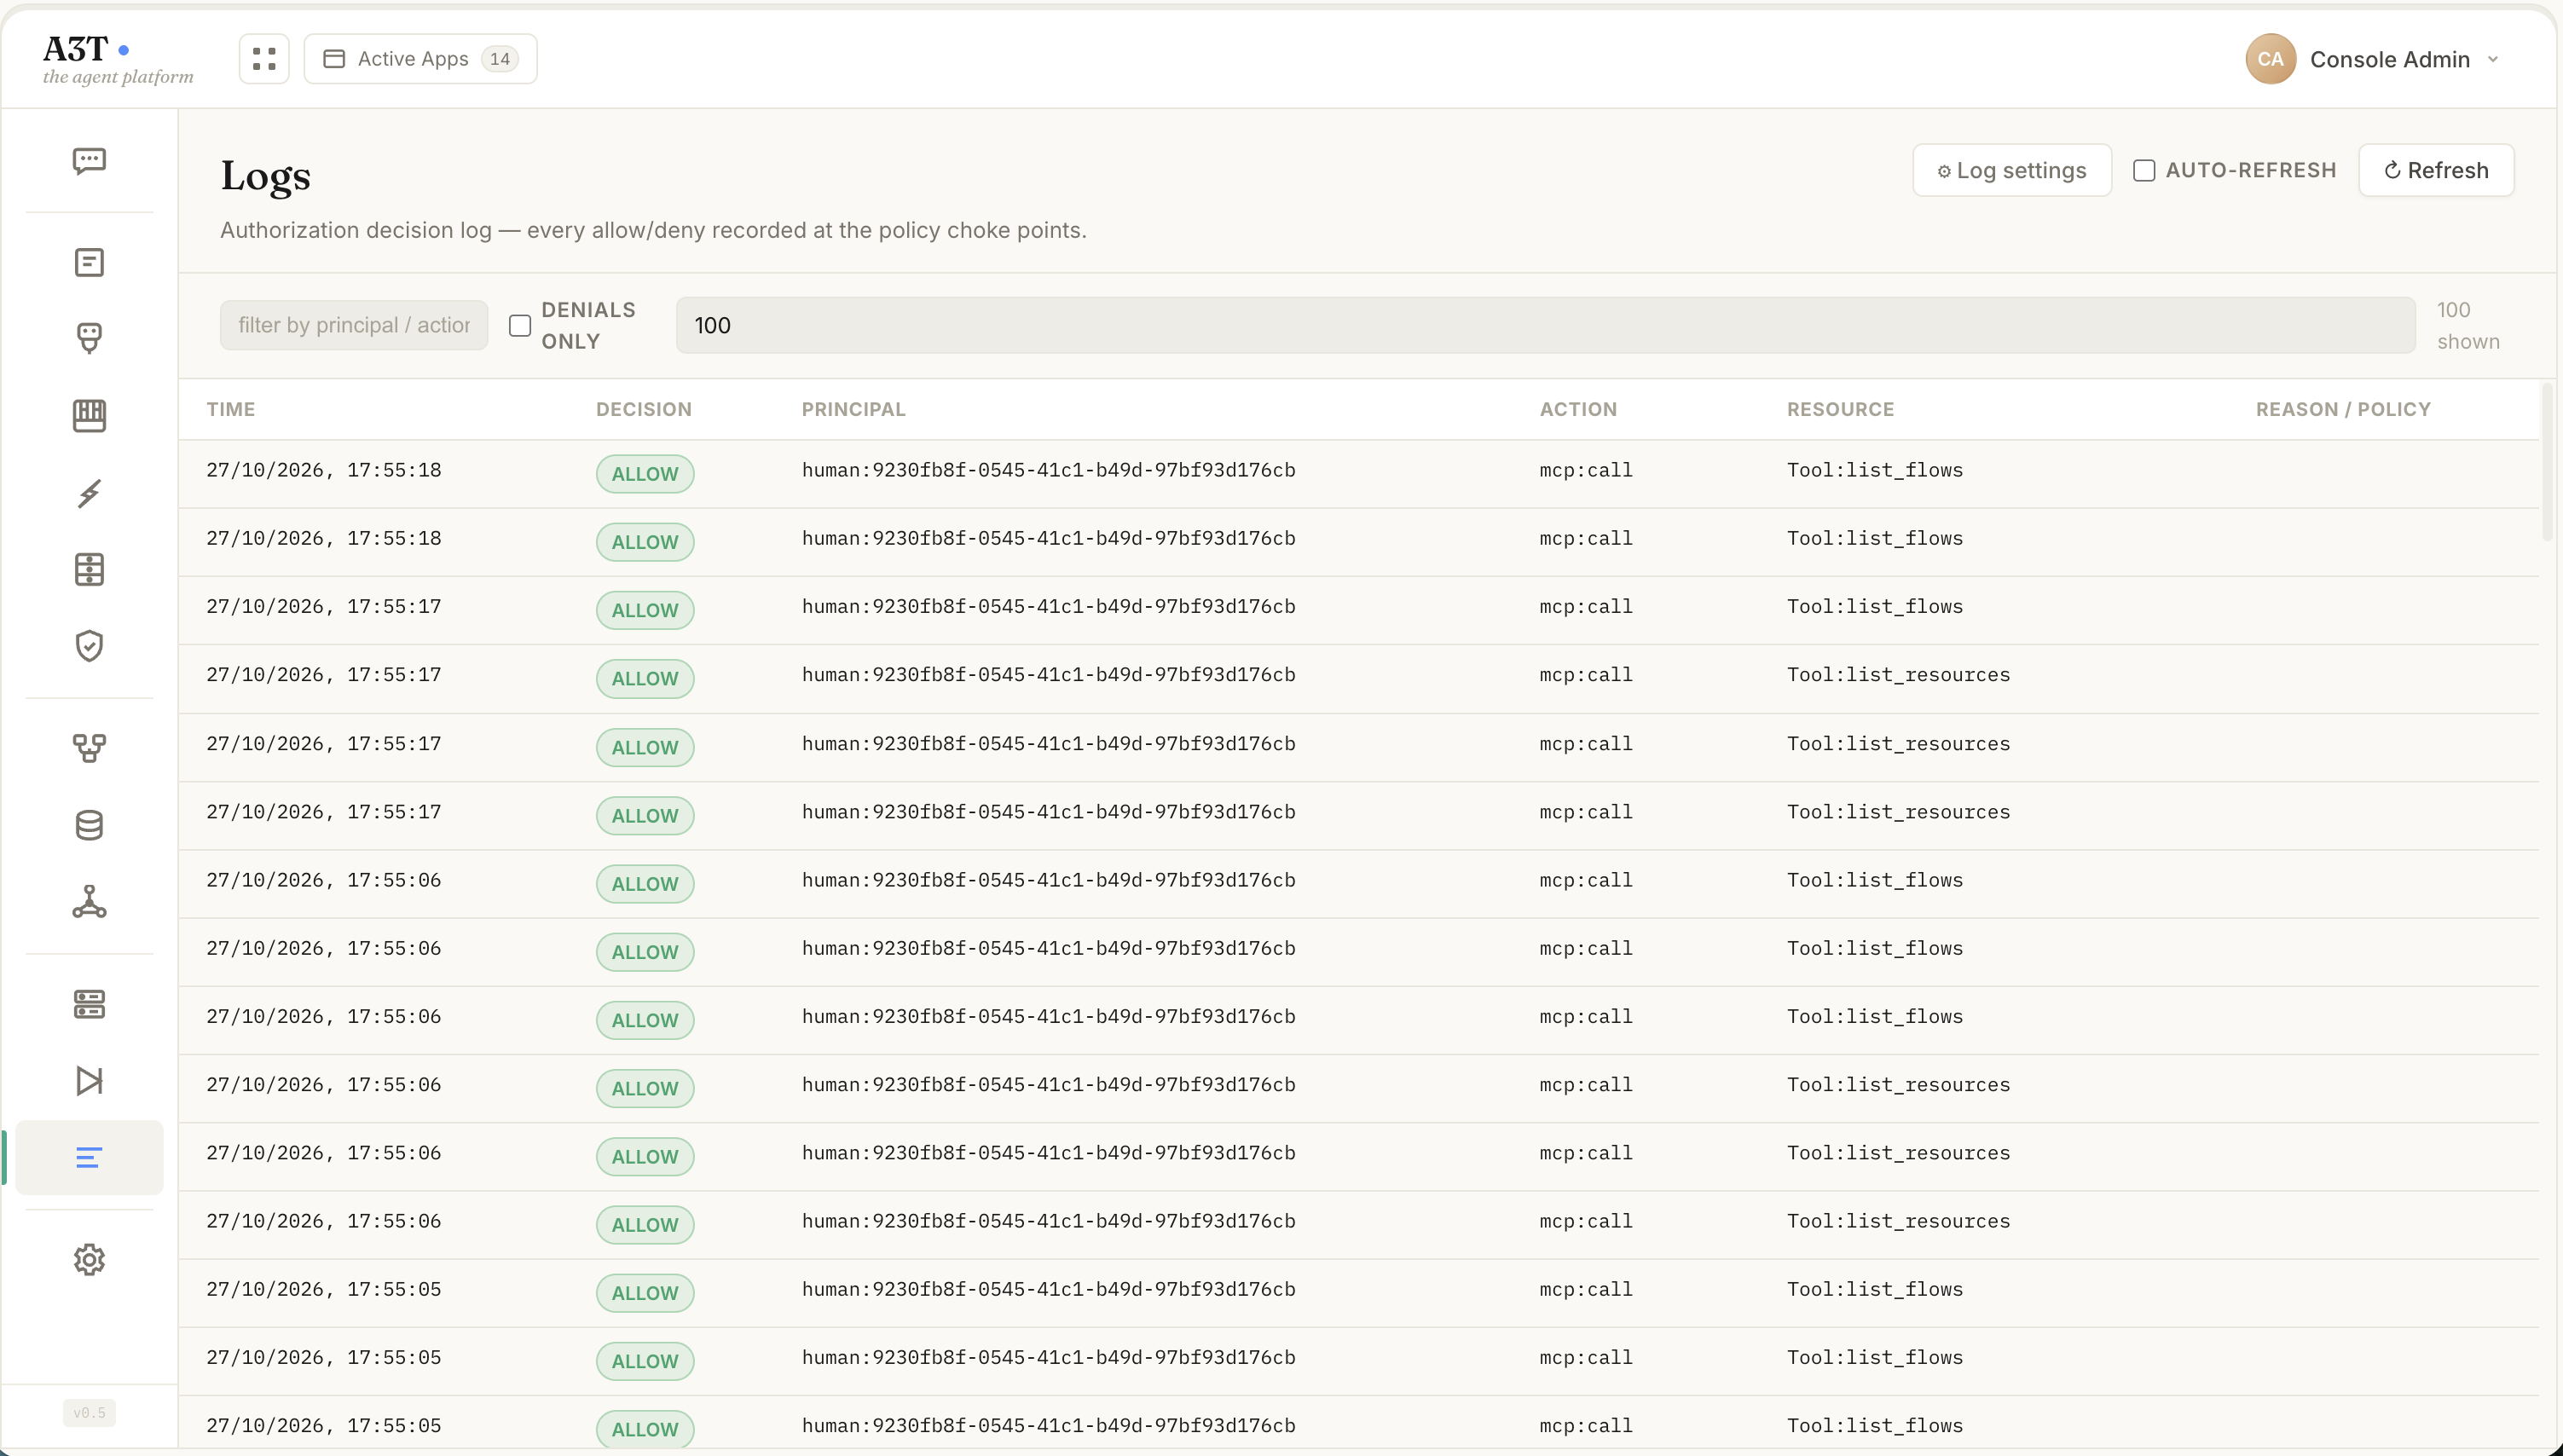
A compiled, deny-by-default Cedar baseline with your own policies layered on top. Dry-run a decision before you ship it; every allow and deny lands in the decision log.
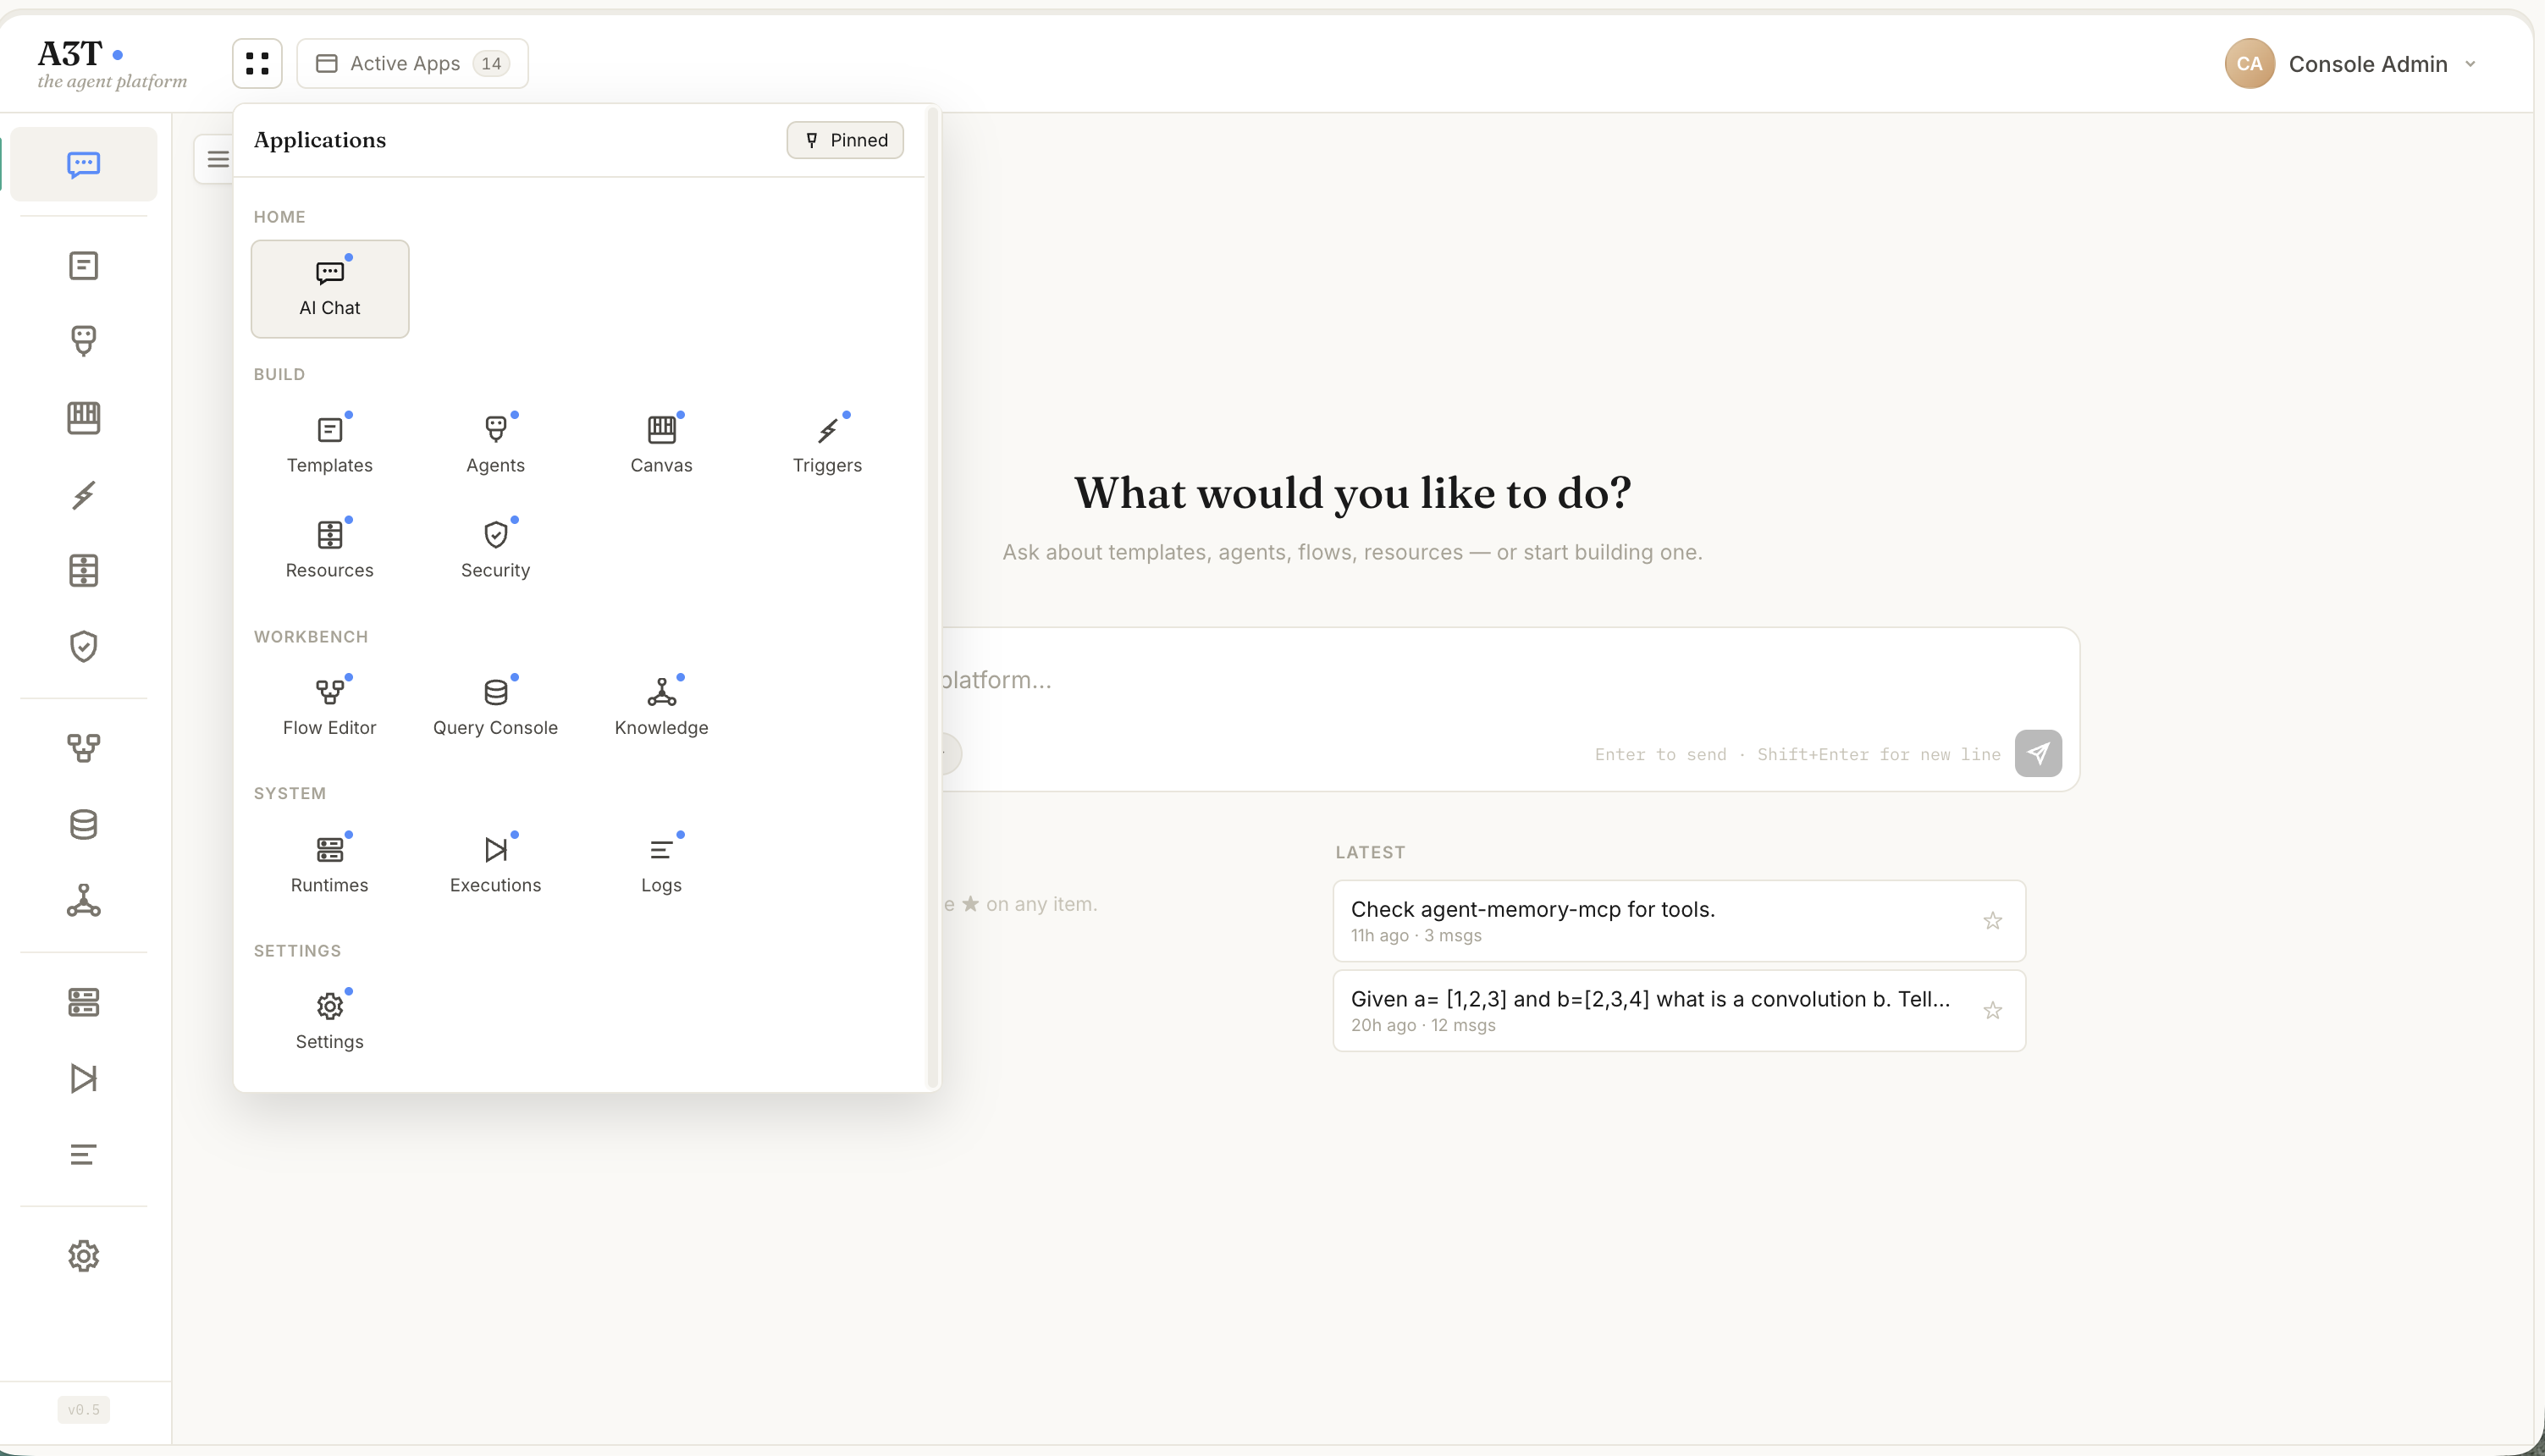
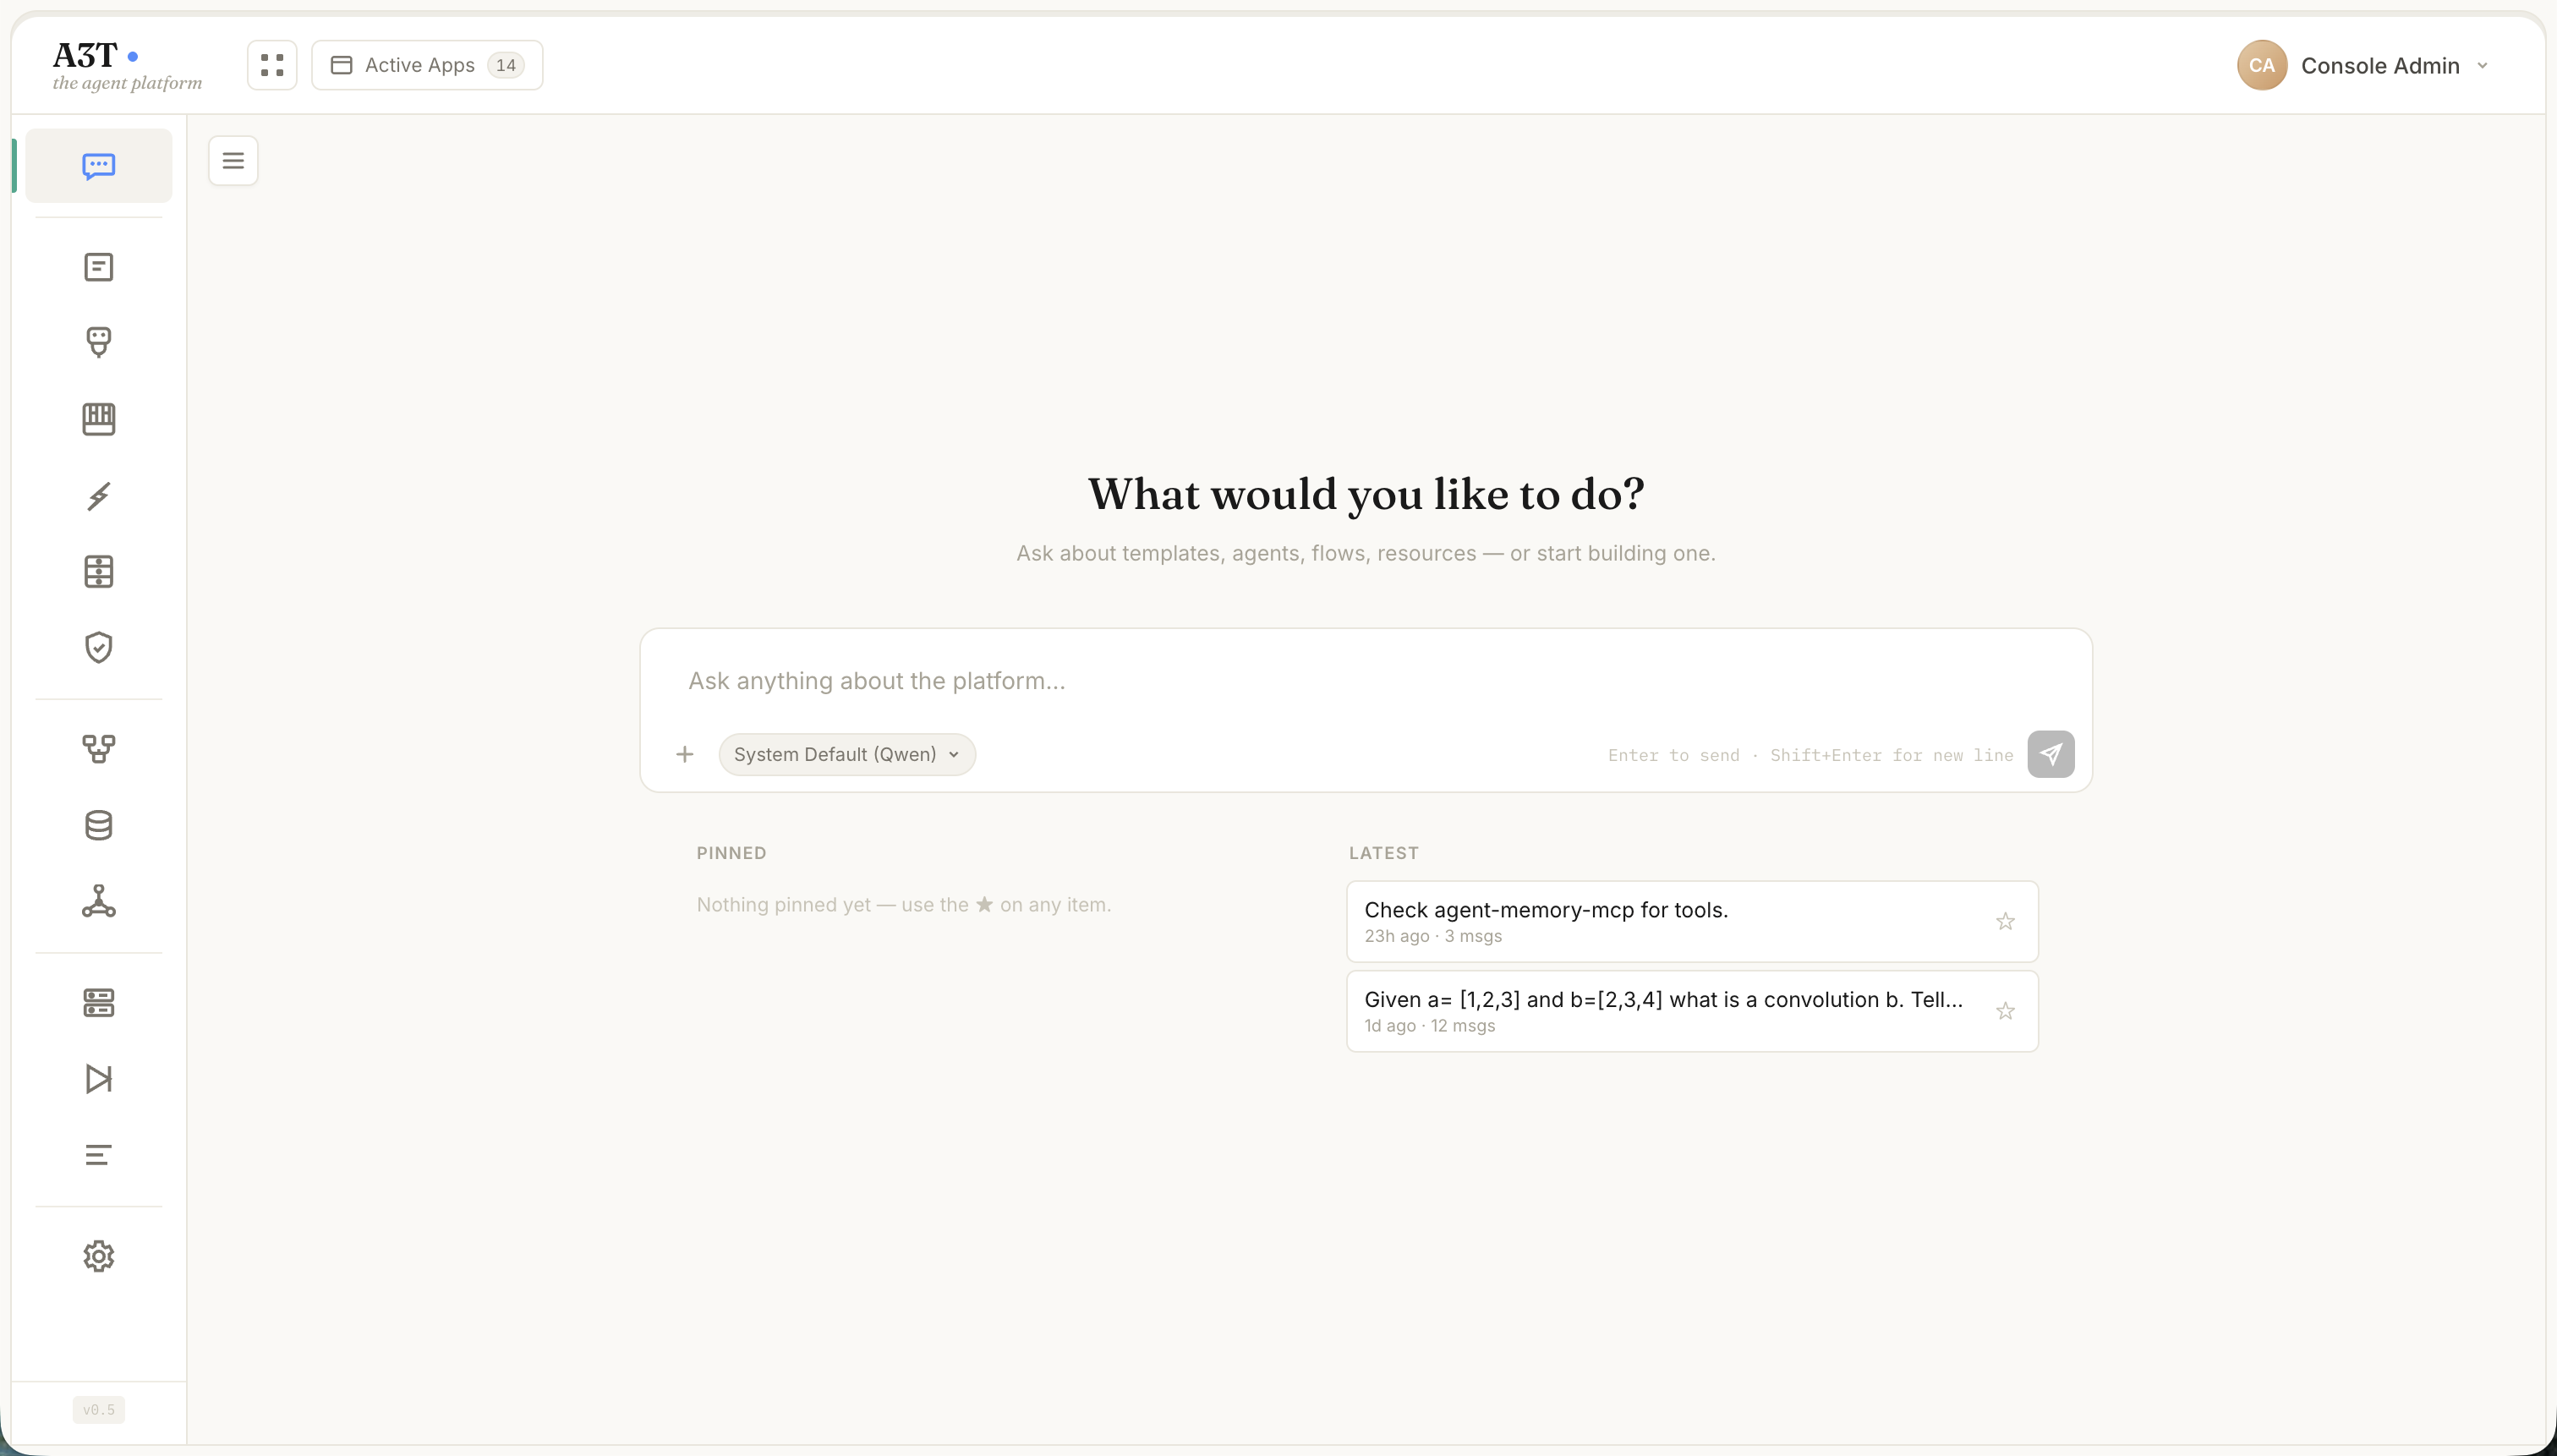
Fifteen apps. One governed control plane.
Build, wire, run and audit from the same place — every app shares the same identity, the same policy engine, the same decision log and the same AgentLM.
Built for the whole organization.
Four perspectives. One governed execution model. Choose your role to see what A3T changes for your team.
Every action has an identity. Every decision has a reason.
Give agents enough access to do real work — without giving them a blank check. Policy follows the user, the agent, and the resource through the entire flow.
- Pluggable OIDC (Keycloak, Entra ID, Okta…) with verified claims
- Per-step Cedar decisions against concrete resources
- Originating identity preserved across nested flows
- Narrow-only capability delegation and deny-by-default
Your cluster. Your runtime. Your operating model.
Run agentic workloads with the same Kubernetes boundaries and operational practices your platform team already uses. Keep infrastructure connections reusable and explicit.
- Rust-based CNCF workflow runtime on Kubernetes
- Namespaced workflows, resources, and triggers
- Webhook, cron and event entry points
- MCP/JSON-RPC control with asynchronous execution polling
Design the memory, not just the pipeline.
Shape the enterprise memory your agents and AgentLM read: what is kept, how it connects, who can see it and how long it lasts.
- Model five memory types and the knowledge graph that links them
- Query everything with AQL: RECALL, STORE, LINK and FORGET
- Scope data per tenant, team and agent, checked by policy
- Set retention and history, with a forget that really deletes
Open standards. From canvas to code.
Build with workflow YAML, named resources, MCP tools, and AQL. Use the console when it helps and your existing development workflow when it doesn’t.
- CNCF Serverless Workflow definitions
- Typed tasks for agents, LLMs, tools, data, and people
- MCP clients for creating, executing, and inspecting flows
- AQL operations to store, recall, forget, and link memory
An agent model that reads
your enterprise memory.
AgentLM reads your enterprise memory directly: past cases, proven procedures and how your systems connect are part of how it thinks, not text pasted into a prompt. That is why it can solve most work itself, inside your tenant. Workflows give it a known path, and policy decides what it may do. Only what it can’t solve is routed to a frontier LLM, and only if policy allows.
- AttendAgentLM reads the relevant enterprise memory directly, as part of how it thinks.
- Solve or routeIt solves the request itself, or routes the hard case to a frontier LLM.
- GovernCedar policy checks every action it takes, routing included, for this agent and this user.
- AnswerIts answer is a typed workflow, checked against the schema before it runs.
- RunThe workflow runs checkpointed and audited.
- LearnVerified outcomes go back to memory, so AgentLM knows more next time.
01 AgentLMEarly access Built-in agent model Reads your memory first.
Before AgentLM does anything, it reads your enterprise memory: past cases, the procedures that worked and how your systems connect. With that context it does the everyday work itself, inside your environment. Only the genuinely hard cases go to a frontier LLM, so costs stay predictable and your data stays where it is.
- Lower, predictable model costs
- Your data stays in your environment
- Answers checked before they run
Show the technical detailsHide the technical details
AgentLM is A3T’s agent model. It runs on a single GPU inside your tenant, reads agent memory directly, and works inside your workflows and policies. Every request starts at a gate where AgentLM decides whether it can solve the request, how much thinking it needs, or whether to escalate to a frontier LLM. Its answer is a workflow that has been checked before it runs.
How it works
- Solve-or-escalate gate. The model’s first layers estimate whether it can solve the request, which skills it needs and how much to think. If agent memory has no matching procedure, evidence or concept, it escalates regardless. A request it keeps costs nothing extra; one it escalates costs a fraction of one pass.
- Reads memory directly. Knowledge-graph nodes are precomputed into attention blocks stored in agent memory. AgentLM attends to them instead of pasting text into a prompt.
- Fixed-size sessions. A session is a fixed-size state plus a short window of recent text, saved to memory after every turn and restored on the next. Each turn processes only its new tokens.
- Answers are workflows. Output is constrained to the CNCF Serverless Workflow schema and dry-run in A3T before it is returned.
- Learns from outcomes. Verified outcomes and workflow changes are written back to memory. A background job consolidates episodes into knowledge for the next request.
- Skills without retraining. Domain and tenant skills are small adapters stored in memory and paged onto the GPU when the gate asks for them. A new domain means training one adapter, not a new model.
Who it helps
Early access covers the core model, memory attention and the solve-or-escalate gate. Skill adapters and trained thinking budgets are on the roadmap.
02 Workflows Workflows that don’t drift Known path, every time.
Workflows run the steps you already know the same way on every run, quickly and reliably, and pick up where they left off if something fails. When a case doesn’t fit, AgentLM handles it and suggests how the workflow should change, so the path improves instead of drifting.
- Reliable, repeatable runs
- Survives failures and restarts
- Improves from its own history
Show the technical detailsHide the technical details
Workflows are written in the open CNCF Serverless Workflow spec and run on a Rust runtime with microsecond dispatch. Inputs are typed, every step is checkpointed, and the execution path is monitored. Only deviations from it go to a model: AgentLM first, a frontier LLM only if AgentLM escalates.
How it works
- Typed inputs. Every workflow declares its input schema, so bad input is caught at the edge instead of halfway through a run.
- 26 task types. Agent, model, MCP tool, human approval, switch, loop, transform, emit and more. Routine steps never spend a token.
- Triggers and sandboxes. Start flows from webhooks, schedules and events, and run tasks in isolated or shared sandboxes.
- Checkpoint and resume. State is saved after every task. A failed or restarted run resumes at the failed step without repeating side effects.
- Monitored execution. Each run is compared with the expected path and recorded as an execution graph in agent memory. That graph is what AgentLM reads to handle a deviation and propose a change.
- Versioned changes. A proposed change becomes a new workflow version once it is approved. The same YAML is on the canvas and in Git.
Who it helps
Example
document:
  dsl: '1.0.0'
  namespace: secops
  name: contain-host
input:
  schema: alert.v2
do:
  - triage:
      call: a3t:agent
      with:
        message: ${ .alert }
03 Memory Enterprise memory Cases, procedures and how they connect.
Your agents keep what they learn: past cases, the procedures that worked, and how people, systems and incidents connect. AgentLM reads it directly, so agents recall instead of asking a model again, and you decide what is kept and what is forgotten.
- No starting from scratch
- Fewer model calls
- Retention you control
Show the technical detailsHide the technical details
Agent memory is one store for everything an agent knows: five memory types, a knowledge graph, and the sessions and attention blocks AgentLM reads directly. It is queried with AQL, the Agent Query Language, and every recall and write is checked against policy.
How it works
- Five memory types. Working, episodic, semantic, procedural and tool memory. Proven procedures are reused, so agents stop asking a model for what they already know.
- AQL. RECALL, STORE, LINK and FORGET. Queries read like what the agent wants to know.
- Knowledge graph. LINK connects memories into a graph agents can traverse, not just a pile of vectors.
- Model memory. AgentLM’s sessions and attention blocks live here too. On a model upgrade they are recomputed from the source data.
- Scopes and sharing. Namespaces keep agents and tenants apart; shared scopes let a team’s agents learn from each other.
- Retention and a real forget. TTLs, history when facts change, and FORGET that actually removes data.
Who it helps
Example
RECALL FROM EPISODIC
  WHERE host = "lt-4471"
  FOLLOW LINKS TYPE "resolved_by"
    INTO PROCEDURAL
  RETURN pattern, confidence
04 Governance Governance on every action Checked before it runs, denied by default.
Each agent has its own identity and acts only within the rules you set, for the people it works for. Anything you haven’t allowed is denied. The same rules cover tools, data and any call to an outside model, and every decision is logged so you can show who did what and why.
- Least privilege for every agent
- Nothing leaves without permission
- A complete audit trail
Show the technical detailsHide the technical details
A Cedar policy engine built into the runtime decides every action before it runs: each task, tool call, memory read and write, and every escalation to a frontier LLM. Agents have their own identities, act on behalf of users, and anything not explicitly allowed is denied.
How it works
- Agents are principals. Each agent has its own service identity, owned by a team, separate from the person who built it.
- On behalf of. When an agent acts for a user, that user’s groups are part of every decision. Agents never see more than the user they act for.
- Deny by default. Anything not allowed is denied, and forbid always wins.
- Escalation is an action. Sending data to a frontier LLM is checked like a tool call, by agent, user and data classification.
- Decision records and dry runs. Every allow and deny is logged with the policy that decided it, and any decision can be dry-run before you ship a change.
- Your identity provider, your secrets. Keycloak, Entra ID or any OIDC provider, with SCIM sync for users and groups. Secrets are resolved at call time and never handed to a model.
Who it helps
Example
forbid (
  principal,
  action == Action::"llm:escalate",
  resource
) when {
  context.data.class == "restricted"
};
Start open. Turn on enterprise when you need it.
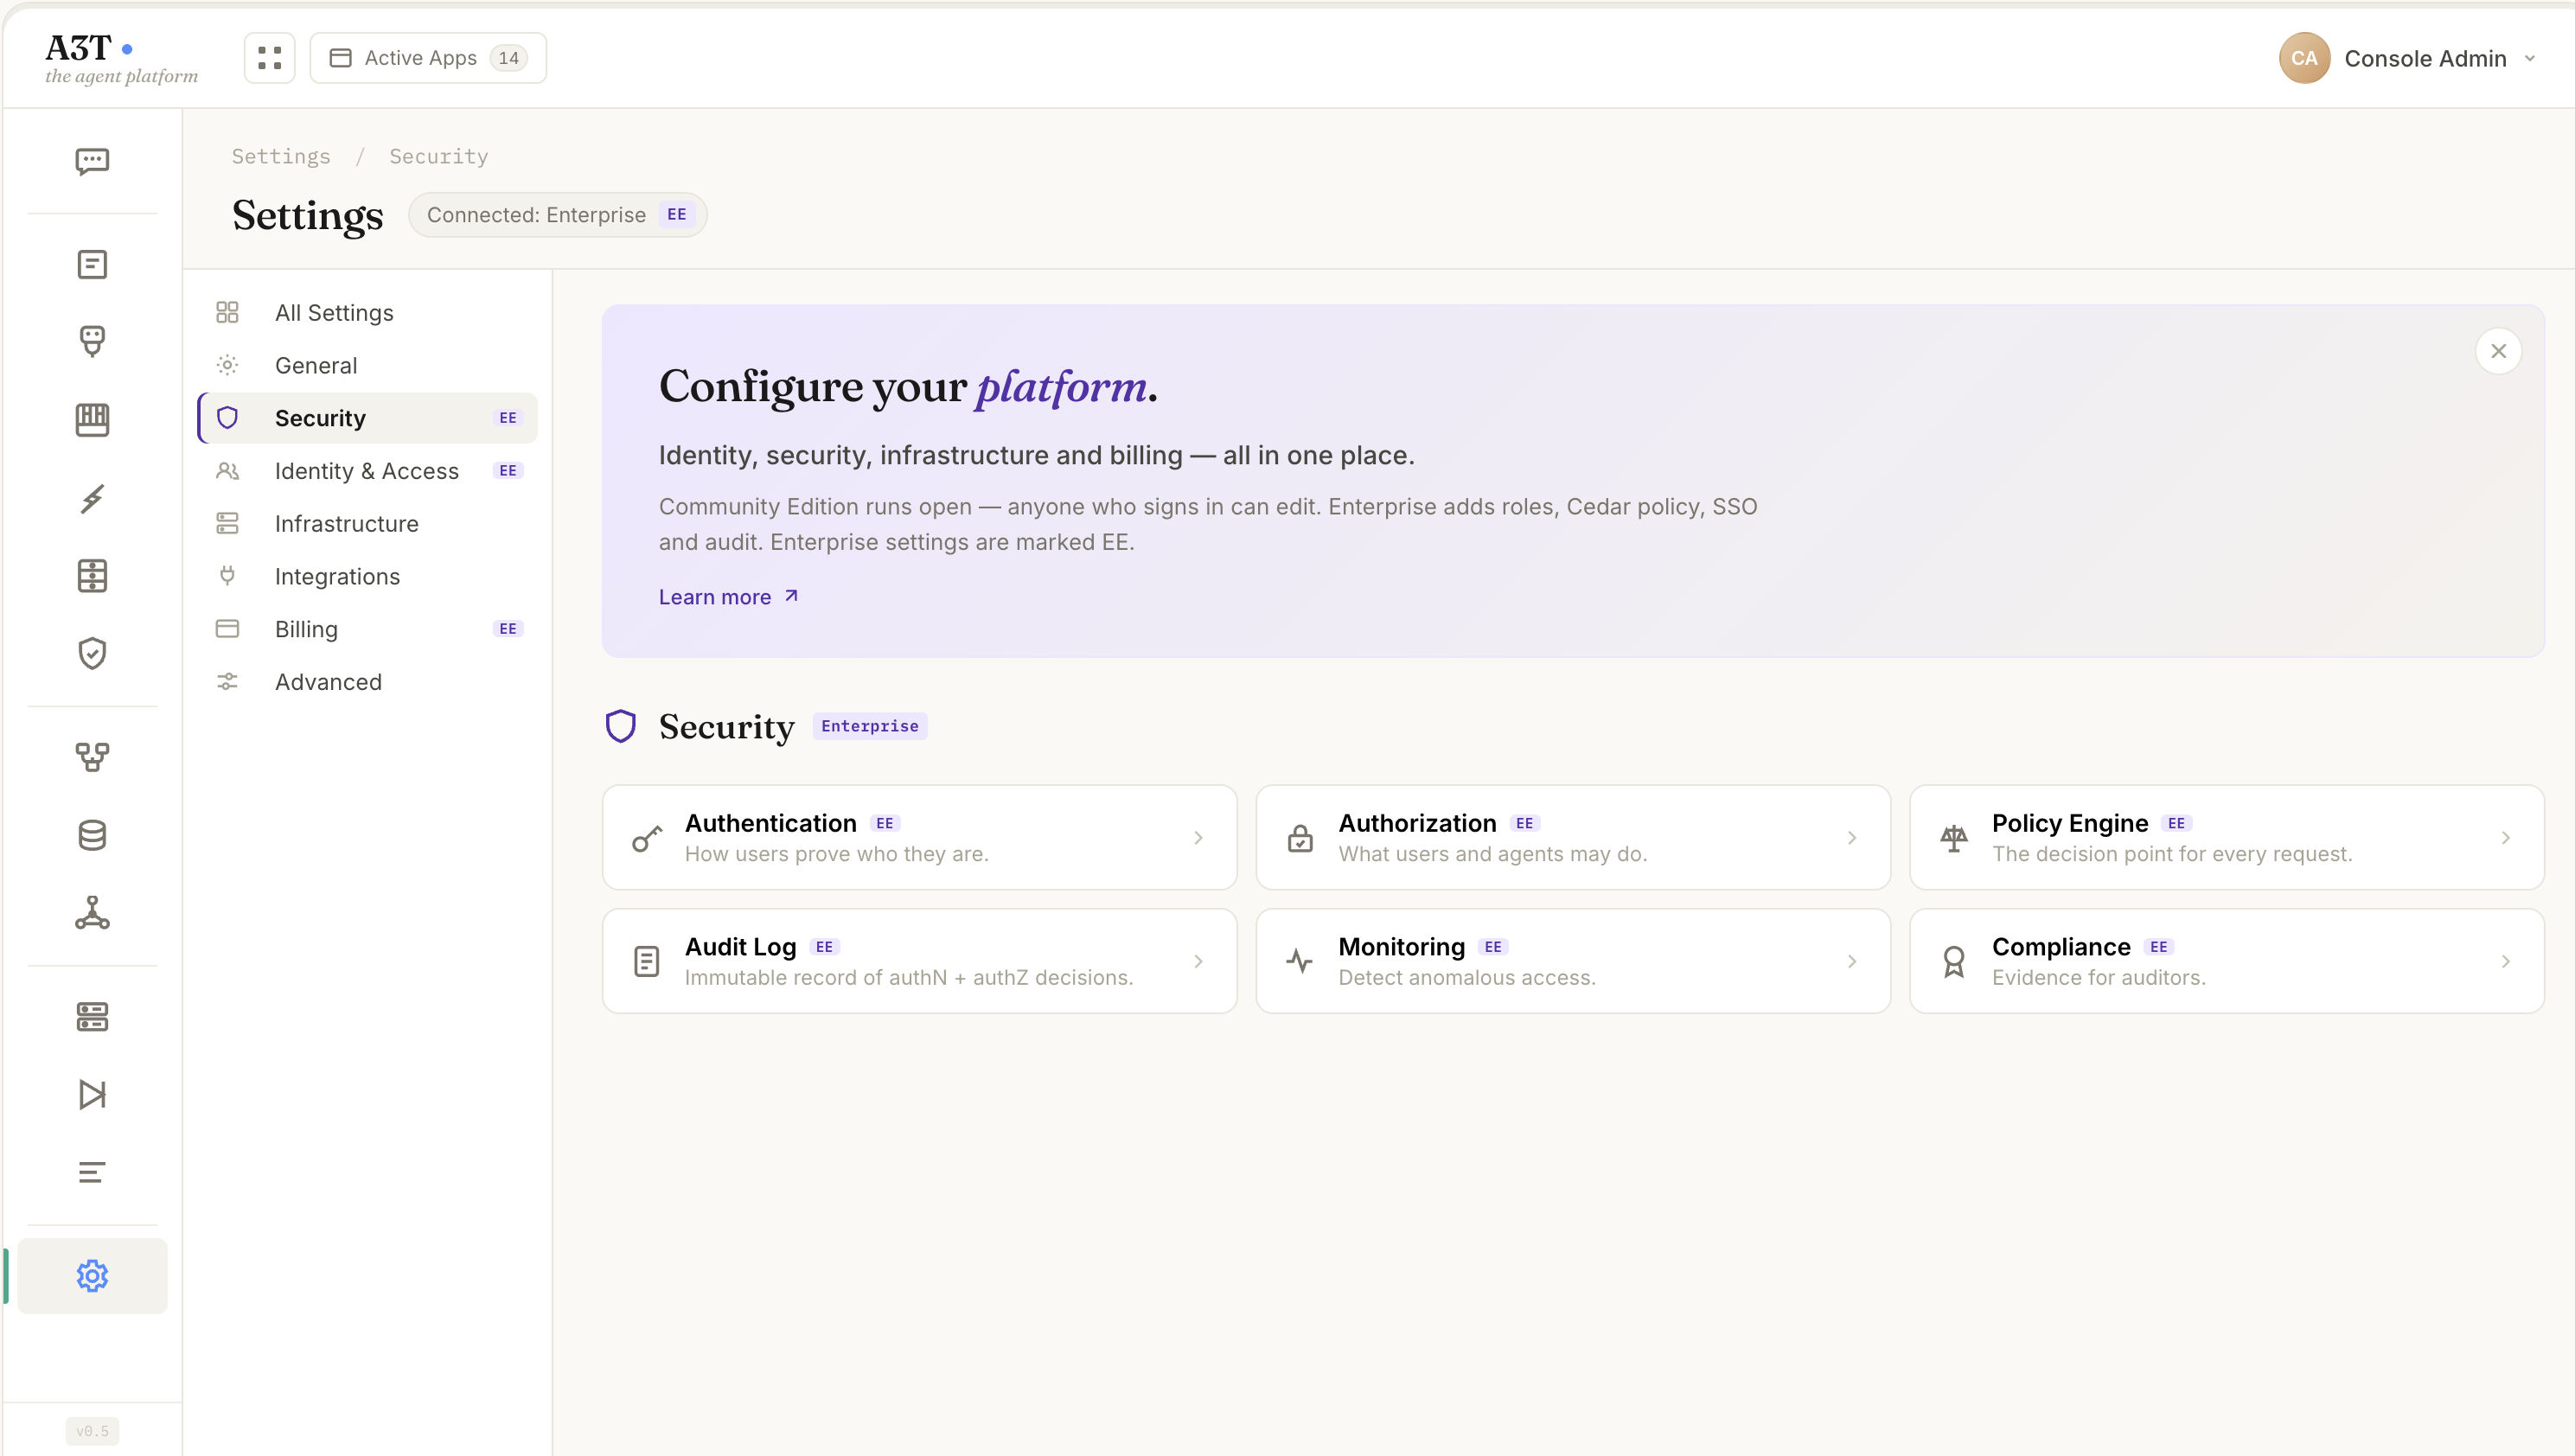
Community Edition runs open — anyone who signs in can edit. Enterprise adds roles, Cedar policy, SSO and audit, configured from one settings page.
Free, self-hosted, embedded storage. Every template, agent and flow feature.
Authentication, authorization, policy engine, audit log, monitoring and compliance.
Give every team its agents. Give your CISO, compliance officer, CMO, COO or CTO a reason to say yes.
Explore the workflow model, inspect the architecture, or open the A3T console to start building.